TotalHealDatasheet · 27 October 2026
TotalHealDNSGuard
DNS Firewall & Security
Stop malware, phishing and DNS tunnelling at the lookup — for every device, on site or on the road.
- Cloud (SaaS)
- Hybrid
- On-premises
- Air-gapped
The challenge
Most malware, phishing and data-theft traffic starts with a DNS lookup. A protective resolver stops the lookup before a connection is made, for every device on a site or on the road, without an agent on every device.
The answer
Threat-blocking protective DNS from the TotalHeal cloud or your own resolver, with blocks and detections landing next to your endpoint alerts. No content-category filtering.
- Status
- Available
- Deploys as
- Cloud (SaaS) · Hybrid · On-premises · Air-gapped
- Runs on
- Cloud resolver (DoH); On-premises resolver node
- Priced per
- Protected user per year
- Trial
- 30 days
- Licence
- Sold on its own; one TotalHeal console
Supported platforms
- BrowsersDoH
- macOS11 and later
- iPhone, iPadDoH profile
- AndroidDoT
- Resolver nodeamd64, arm64
How it works
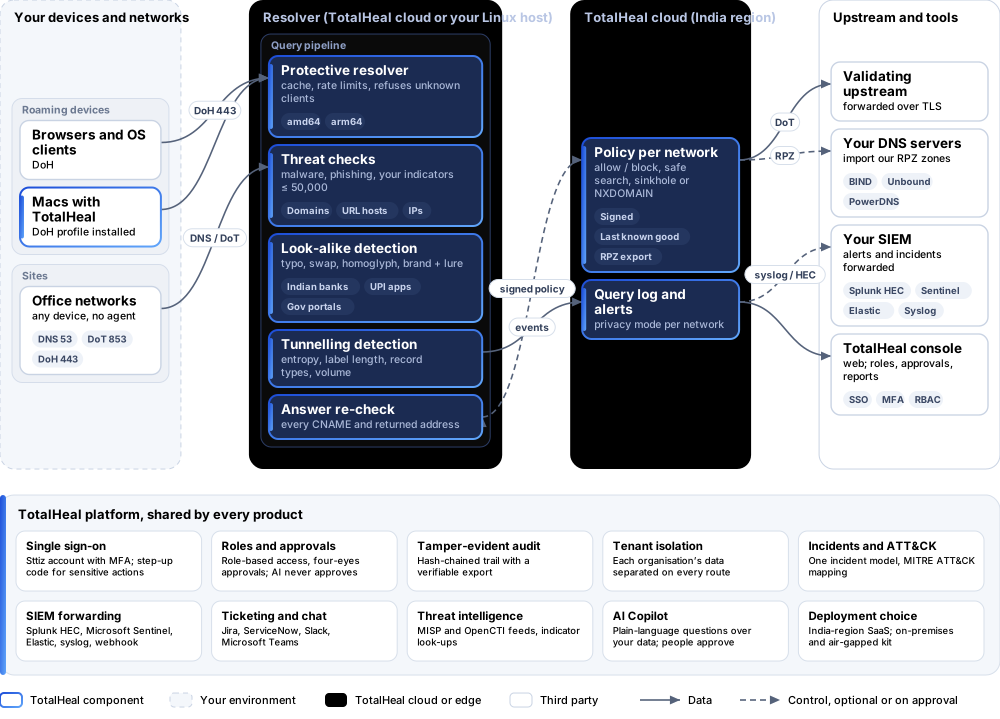
- PointSend devices to the cloud resolver by DoH, or run the resolver on your own Linux host.
- CheckEach lookup is checked against threat lists, your indicators, look-alikes and new domains.
- Re-checkEvery CNAME target and returned address is checked too.
- Block or detectSinkhole or NXDOMAIN with a standard Blocked code, or detect only, per policy.
Reference architecture
Key capabilities
- Malware and phishing domainsKnown malicious hosts blocked; shared platforms such as GitHub or Drive are never listed, because DNS cannot see a path.
- Your own threat intelYour domains, URL hosts and IP addresses as blocking triggers — up to 50,000 indicators.
- Look-alike detectionTypo-squats, swapped letters, homoglyphs (including Cyrillic) and brand-plus-lure names, with Indian banks, payment apps and government portals built in.
- New and never-seen domainsNewly registered domains (with a feed) and domains your organisation has never looked up before.
- DNS tunnelling and exfiltrationDetected from entropy, label length, record types and volume; detect or block per policy.
- Answers are checked tooEvery CNAME target and returned address is re-checked.
- Policies per networkAllow and block lists, safe search for Google, Bing, DuckDuckGo and YouTube, sinkhole or NXDOMAIN, with a standard “Blocked” error code.
- Standard formatsEvery list is a standard RPZ zone you can export for BIND, Unbound or PowerDNS. DoH in the cloud; DNS, DoT and DoH on your own resolver.
- Never an open resolver, never fails openUnknown clients refused, rate limits, zone transfers refused; signed policy bundles with last-known-good. Privacy modes per network; BYOD networks never log allowed queries.
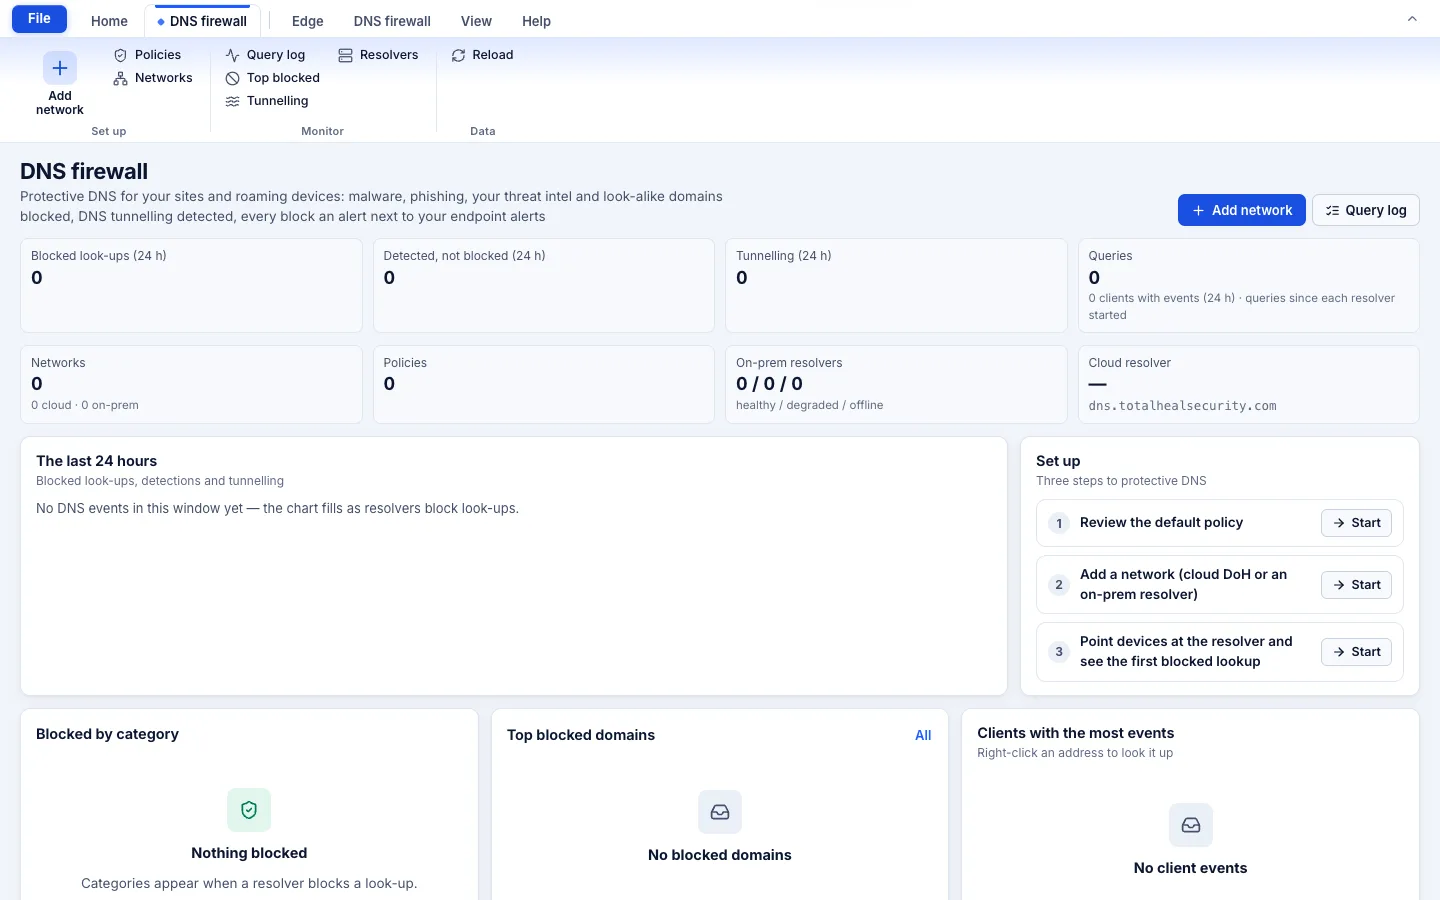
In the console
Deployment options
Cloud (SaaS)AvailableRuns as a test deployment for listed organisations.
HybridAvailableThe installer stays locked until the release key is published.
On-premisesAvailableDelivered with our team from the on-premises kit.
Air-gappedAvailableOffline kit, offline licence file and offline update bundles.
System requirements
Protected platforms
- BrowsersDoH
- macOS11 and later
- iPhone, iPadDoH profile
- AndroidDoT
- Resolver nodeamd64, arm64
On-premises server
- Operating system
- RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12
- Processor
- 4 vCPU (tested configuration)
- Memory
- 8 GB recommended (6 GB minimum)
- Disk
- 10 GB free for software, releases and backups, plus data
- Sign-in
- Active Directory / LDAP, SAML 2.0 or OpenID Connect
- Software
- Nothing to pre-install: no container runtime, database, web server or Java
Network and access
- Cloud: a client that speaks DoH
- On-premises: a Linux host with systemd, outbound HTTPS, a TLS certificate for DoT/DoH, a Professional or Elite licence
Alerts and tickets to
- Splunk
- Microsoft Sentinel
- Elastic
- Syslog / CEF
- Jira
- ServiceNow
- Slack
- Microsoft Teams
Technical specifications
| Features | Included | ||
|---|---|---|---|
| Malware and phishing domains | Included | ||
| Your own threat intel | Included | ||
| Look-alike detection | Included | ||
| New and never-seen domains | Included | ||
| DNS tunnelling and exfiltration | Included | ||
| Answers are checked too | Included | ||
| Policies per network | Included | ||
| Standard formats | Included | ||
| Never an open resolver, never fails open | Included | ||
| Availability by tier | Essential | Professional | Elite |
| Cloud DoH resolver, threat categories, safe search, allow and block lists, tunnelling detection, query log, alerts, RPZ export | Included | Included | Included |
| Secure DNS on TotalHeal desktop agents | Included | Included | Included |
| On-premises resolvers (DNS, DoT, DoH, block page) | — | Included | Included |
| Threat-actor and campaign intelligence | — | — | Included |
| List price per user per year | US$18 · ₹1,710 | US$36 · ₹3,430 | US$54 · ₹5,140 |
| Platforms and coverage | |||
| Cloud resolver (DoH) | Any client that speaks DoH: browsers, macOS/iOS by profile; the TotalHeal app on macOS installs the profile | ||
| On-premises resolver node | Linux amd64/arm64 with systemd (Professional and Elite) | ||
| Deployment options | |||
| SaaS (cloud DoH resolver, India) | AvailableRuns as a test deployment for listed organisations. | ||
| Hybrid (your resolver, TotalHeal console) | AvailableThe installer stays locked until the release key is published. | ||
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. | ||
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. | ||
| Licensing | |||
| Priced per | Protected user per year | ||
| Counted | Distinct users or devices seen by the resolver | ||
| Trial | 30 days | ||
| Government profile | Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks. | ||
| Procurement dossier | Compliance matrix, bill of materials, architecture and hardening, SLA and OEM authorisation letter, on request | ||
| On-premises server | |||
| Operating system | RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12 | ||
| Processor | 4 vCPU (tested configuration) | ||
| Memory | 8 GB recommended (6 GB minimum) | ||
| Disk | 10 GB free for software, releases and backups, plus data | ||
| Sign-in | Active Directory / LDAP, SAML 2.0 or OpenID Connect | ||
| Software | Nothing to pre-install: no container runtime, database, web server or Java | ||
| Requirements | |||
| Requirement 1 | Cloud: a client that speaks DoH | ||
| Requirement 2 | On-premises: a Linux host with systemd, outbound HTTPS, a TLS certificate for DoT/DoH, a Professional or Elite licence | ||