TotalHealEvidenceLensDigital Forensics & Triage
Collect triage evidence from an endpoint or server during an investigation, with chain of custody.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate EvidenceLens Digital Forensics. No card.
During an incident the first questions are what was running, what was connected and what starts at boot — and the answers vanish when a machine is rebooted or cleaned. Evidence collected ad hoc, by hand, is hard to defend later.
EvidenceLens takes a volatile-state snapshot from an endpoint or server on a signed command from the console, shows the collection to the person at the device, and keeps the evidence with a chain of custody.
EvidenceLens Digital Forensics, feature by feature.
Volatile-state snapshot
Running programs, network connections and startup items from the moment of collection — no file contents.
Only on a signed command
Collection starts only from a signed command issued in the console, and is shown to the person at the device.
Chain of custody
Each collection is recorded with who asked, when, from which device and its integrity hash.
Part of the investigation
Snapshots attach to the incident they were taken for, next to the alerts and timeline.
How EvidenceLens Digital Forensics works.
EvidenceLens collects a volatile-state snapshot — running programs, connections, startup items — from an endpoint or server on a signed command, shows the collection to the person at the device, and keeps it with a chain of custody.
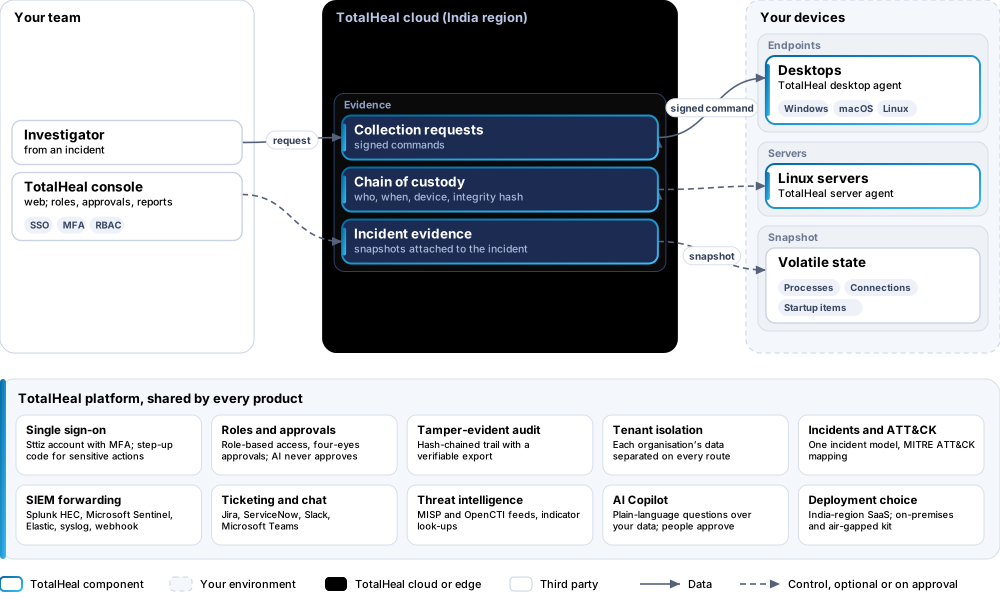
- RequestAn investigator asks for a snapshot from an incident.
- CollectThe agent captures processes, connections and startup items.
- RecordCustody details and the integrity hash are recorded.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Windows, macOS, Linux desktops | TotalHeal desktop agent |
| Linux servers | TotalHeal server agent |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | AvailableSingle-region service. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Unit and tiers.
Priced per endpoint per year. Counted: devices that can be collected from. List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| Triage snapshots on signed command, chain of custody | Included | Included |
| Disk and memory acquisition | — | Roadmap |
| Price | Contact sales | Contact sales |
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- A TotalHeal agent on the endpoint or server (any TotalHeal agent licence)
- An EvidenceLens licence
Procurement documents for EvidenceLens Digital Forensics
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
TotalHealThreatFusion
Extended Detection & Response (XDR)
One incident across endpoint, network, identity, email and cloud — with or without our EDR.
TotalHealThreatGuard
Business Antivirus (NGAV / Endpoint Protection)
Business antivirus on the TotalHeal agent: stop known malware without quarantining legitimate work.
Get a quote for EvidenceLens Digital Forensics.
Tell us how many endpoints you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.