TotalHealTrafficShieldBot management & L7 DDoS
Keep bots, credential stuffing and application-layer (Layer 7) floods off your sites.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate TrafficShield Bot management & L7 DDoS. No card.
Public sites and sign-in pages are hit by automated clients: scrapers, credential-stuffing tools and application-layer floods that send ordinary-looking requests until the site slows down or falls over.
The TotalHeal edge tells people from scripts, protects sign-in pages from credential stuffing and escalates by itself during a Layer 7 flood — with its own browser check, no CAPTCHA vendor in the path.
TrafficShield Bot management & L7 DDoS, feature by feature.
Bot score for every request
Headers, header order, client hints, behaviour and headless or automation signals (and TLS fingerprints when TLS ends at the edge) give each client a score: human, unknown, automated or verified crawler.
Verified search crawlers
Search crawlers are verified by reverse DNS; clients that only claim to be a crawler are flagged.
Own browser check, no CAPTCHA
A self-hosted browser check and proof-of-work challenge with no third-party script; a person passes it without doing anything and gets a clearance for an hour.
Log first, enforce when ready
Bot management starts by scoring and reporting only; switching an app to enforce needs a reason and is audited.
Credential-stuffing protection
One address trying many user names with many failures on a sign-in page — or a wave spread across addresses — is detected, then challenged or blocked.
Adaptive Layer 7 DDoS
A learned traffic baseline per app and path; under a flood the edge escalates by itself from elevated to under attack (every client without clearance is checked), and steps down when the flood is over.
Under-attack mode
Turn on under-attack mode by hand for up to 72 hours, with a reason; it is audited.
Measured on our test edge
In our 25 Oct 2026 run, a 70-requests-a-second page flood was challenged 21.6 seconds after it started and none of it reached the site after that; every real browser that was checked during the attack passed on its own; a credential-stuffing replay was flagged after 8 failed sign-ins.
Alerts next to your other alerts
Bot, credential-stuffing and flood detections become alerts with MITRE ATT&CK mapping, with bot traffic, top clients, sign-in attempts and attack episodes in the console.
How TrafficShield Bot management & L7 DDoS works.
TrafficShield scores every request at the TotalHeal edge, protects sign-in pages from credential stuffing and escalates on its own during an application-layer flood — with its own browser check and no CAPTCHA vendor. In our 25 Oct 2026 test a page flood was challenged 21.6 seconds after it began and none of it reached the site afterwards.
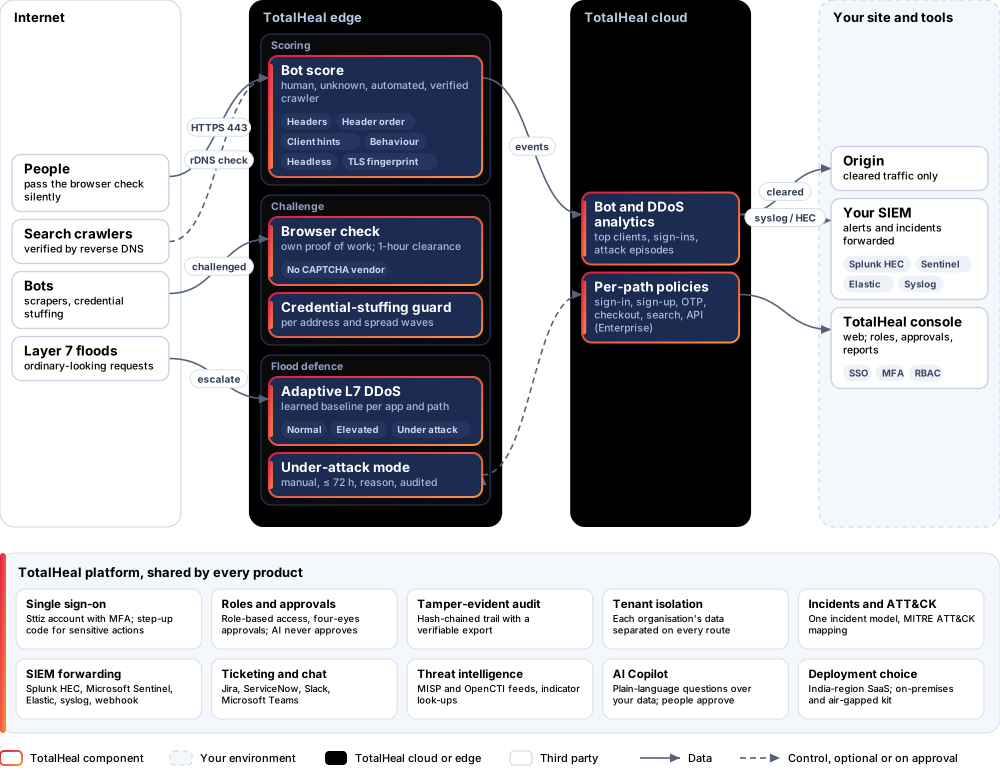
- ScoreEvery request gets a bot score: human, unknown, automated or verified crawler.
- LogBot management starts in log mode; enforcing needs a reason and is audited.
- ChallengeSuspicious clients get the self-hosted browser check; people pass without doing anything.
- EscalateUnder a flood the edge moves from elevated to under attack, then steps down when it ends.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| SaaS | Any web application over HTTP(S) behind the TotalHeal edge: verify the domain, point a CNAME at the edge |
| Self-hosted edge node | Linux with systemd, x86_64 or aarch64 (Professional and Elite) |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (CNAME to the TotalHeal edge, India) | AvailableNo production point of presence with high availability yet. |
| Hybrid (self-hosted Linux edge node) | AvailableThe installer stays locked until the release key is published. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Essential, Professional or Elite.
Priced per protected application (fqdn) per year. Counted: applications configured.
| Feature | EssentialUS$2,400per application per year | ProfessionalUS$7,200per application per year | EliteUS$18,000per application per year |
|---|---|---|---|
| Bot score, verified crawlers, log or enforce, browser and proof-of-work checks | |||
| Credential-stuffing protection on sign-in pages | |||
| Adaptive Layer 7 DDoS protection, under-attack mode, attack episodes and history, alerts | |||
| Per-path bot policies (sign-in, sign-up, OTP, checkout, search, API) | |||
| Self-hosted edge nodes in your data centre | |||
| Threat-actor and campaign intelligence on attacking addresses |
List prices per application per year; minimum 1 application. Each tier includes everything in the tier before it. Volume, multi-product and partner pricing on request.
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- The TotalHeal edge in front of your site (TotalHeal point of presence, or a self-hosted edge node on Professional and Elite)
- SaaS: a DNS TXT record and a CNAME for each protected domain; the origin reachable from the TotalHeal edge
Procurement documents for TrafficShield Bot management & L7 DDoS
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
Part of TotalHeal Edge Defense suite and of Complete — each product is still licensed on its own.
Get a quote for TrafficShield Bot management & L7 DDoS.
Tell us how many protected application (fqdn)s you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.