TotalHealCloudPostureCloud Security Posture Management (CSPM)
Find risky settings in your AWS, Azure and Google Cloud accounts — connected without keys.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate CloudPosture CSPM. No card.
Public storage buckets, administrators without MFA and roles anyone can assume are the commonest cloud breaches, and most security tools want a long-lived access key to look for them — one more secret to leak.
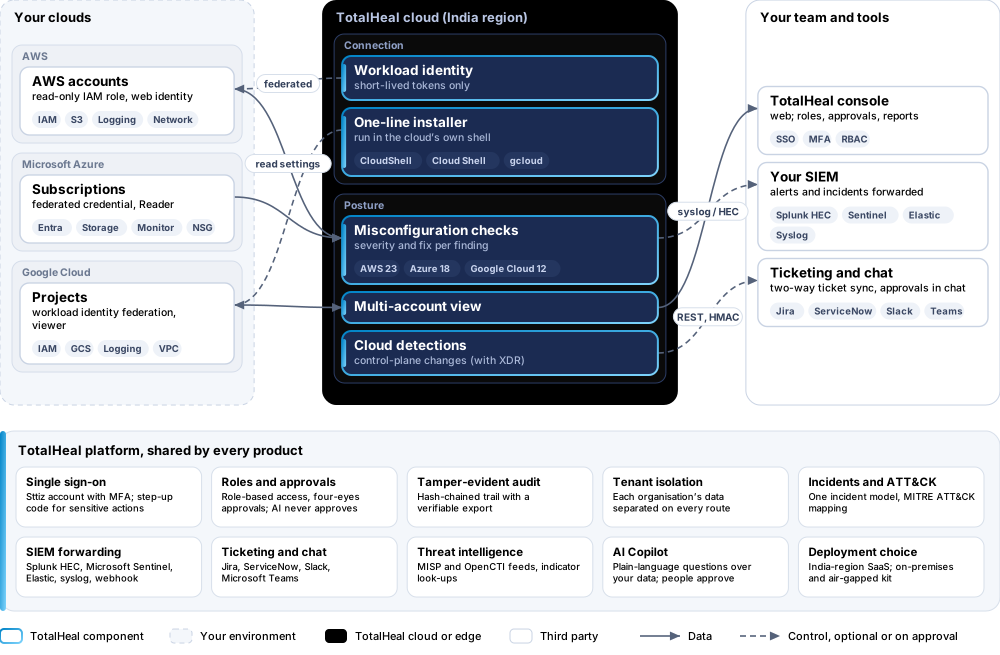
CloudPosture connects to each cloud account without keys: a one-line installer in the cloud’s own shell makes the account trust TotalHeal, read-only. It then checks the account’s settings and lists what is risky, account by account.
CloudPosture CSPM, feature by feature.
Keyless connection
For AWS, Azure and Google Cloud a one-line installer run in the cloud’s own shell creates a read-only trust for TotalHeal. No access key, secret or key file is created or stored.
Misconfiguration checks
Checks across identity, storage, logging and network settings — 23 for AWS, 18 for Azure and 12 for Google Cloud — such as public buckets, console users without MFA, old access keys and roles any account can assume.
Per account and across accounts
Findings per account with severity and how to fix them, and a multi-account view.
Cloud detections
Cloud audit-log rules for control-plane changes join incidents when ThreatFusion XDR is present.
How CloudPosture CSPM works.
CloudPosture connects to AWS, Azure and Google Cloud through read-only trust created by a one-line installer in the cloud’s own shell — no access key or secret is ever created — and checks each account for the misconfigurations behind most cloud breaches.
- ConnectRun the one-line installer in the cloud’s own shell.
- CheckIdentity, storage, logging and network settings are checked.
- PrioritiseFindings per account with severity and the fix.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Amazon Web Services | Read-only role trusted by TotalHeal |
| Microsoft Azure | Read-only access through workload identity federation |
| Google Cloud | Read-only access through workload identity federation |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | AvailableSingle-region service. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Unit and tiers.
Priced per cloud account per year. Counted: connected cloud accounts, subscriptions or projects. List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| Keyless connection, misconfiguration checks, multi-account view | Included | Included |
| Price | Contact sales | Contact sales |
No Business/Enterprise split is set for CloudPosture yet.
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- Someone who may create a read-only role or federation in each cloud account
Procurement documents for CloudPosture CSPM
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
TotalHealThreatFusion
Extended Detection & Response (XDR)
One incident across endpoint, network, identity, email and cloud — with or without our EDR.
TotalHealLogIntelligence
SIEM & Log Management
Collect, search and alert on logs from firewalls, DNS servers, servers and identity providers.
Get a quote for CloudPosture CSPM.
Tell us how many cloud accounts you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.