TotalHealSaaSPostureSaaS Security Posture Management (SSPM)
Checks the security settings of your Microsoft 365 and Google Workspace tenants continuously — MFA, administrators, app consent, sharing, third-party apps — and fixes them with a second person’s approval.
Trial: 30 days, up to 50 users. You sign in to the TotalHeal console with a Sttiz account and activate SaaSPosture SSPM. No card.
Most breaches of Microsoft 365 and Google Workspace come from settings, not exploits: MFA that is registered but not required, legacy protocols that skip it, an administrator nobody uses, people allowed to grant any app access to their mailbox, files shared with links anyone can open. Settings drift as admins change them, and nobody notices until an attacker does.
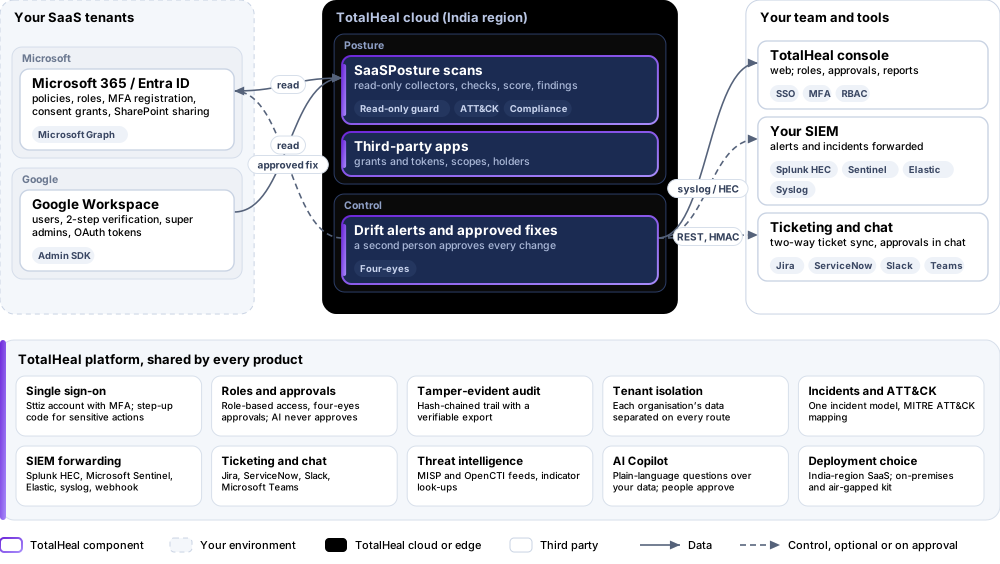
SaaSPosture reads the settings of your Microsoft 365 / Entra ID and Google Workspace tenants through the connectors you already have, with read-only access, and checks them continuously. Each failing setting is a finding with the fix, its MITRE ATT&CK techniques and the compliance controls it maps to. The Professional tier adds the third-party app inventory and drift alerts; the Elite tier applies fixes after a second person approves.

SaaSPosture SSPM, feature by feature.
Microsoft 365 / Entra ID checks
MFA enforced for all users (security defaults or Conditional Access), people and administrators without MFA, legacy authentication blocked, Global Administrator count from two to five, user consent to apps, guest invitations, user app registration and tenant creation, SharePoint and OneDrive Anyone links.
Google Workspace checks
2-step verification enforced and enrolled, super administrators without 2-step verification, super administrator count from two to four, super administrators unused for 90 days, third-party apps with high-risk access.
Read-only by design
Scans use read permissions only, and every scan request is checked before it leaves TotalHeal: anything that is not a read is refused. A setting the connector may not read is reported as not evaluated with the permission it needs — never guessed.
A score and a fix for every finding
A severity-weighted score per tenant and overall, findings worst first, the steps to fix each one in the admin centre, and a trend. Accept a risk with a reason and an optional end date; it reopens by itself.
Mapped to frameworks
Each check maps to MITRE ATT&CK techniques and to controls of NIST 800-53, NIST CSF, ISO 27001, SOC 2, PCI DSS, CIS v8, DPDP and other packs in TotalHeal Compliance.
Third-party app inventory
Every app people granted delegated access (Microsoft 365) or OAuth tokens (Google Workspace): its publisher and whether it is verified, its scopes in plain words, and how many people — or everyone, by administrator consent — granted it. Apps that can read or send mail, read or change every file, or change the directory come first.
Drift alerts
After a clean scan, a critical or high setting that starts failing raises an alert in the same incident queue as endpoint, identity and cloud alerts, and goes on to your SIEM, ticketing and playbooks.
Fixes with four-eyes approval
Request a fix — stop users consenting to apps, allow only administrators and Guest Inviters to invite guests, revoke an app’s access — and a different person approves it before TotalHeal makes the change with the connector’s credentials. Both decisions are kept in the audit log, and the tenant is scanned again.
How SaaSPosture SSPM works.
SaaSPosture reads the security settings of your Microsoft 365 / Entra ID and Google Workspace tenants with read-only access and checks them continuously: MFA, administrators, legacy authentication, app consent, guests, sharing and third-party apps. Every failing setting comes with the fix; drift raises an alert; and fixes TotalHeal applies need a second person’s approval.
- ConnectUse the Microsoft 365 or Google Workspace connector you already have, with the read permissions listed for each check.
- ScanSettings, administrators, MFA registration and third-party apps are read and checked; anything unreadable is named with its permission.
- PrioritiseFindings come worst first, with a score per tenant, the fix and the frameworks they map to.
- WatchScans repeat; a setting that drifts back raises an alert.
- FixFix it yourself from the steps, or request a fix that a second person approves before TotalHeal applies it.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Microsoft 365 / Entra ID | App registration with Microsoft Graph application permissions AuditLog.Read.All, Directory.Read.All, Policy.Read.All; SharePointTenantSettings.Read.All, DelegatedPermissionGrant.Read.All and Application.Read.All for sharing and apps |
| Google Workspace | Service account with domain-wide delegation for admin.directory.user.readonly and admin.directory.user.security |
| Fixes (Elite) | Policy.ReadWrite.Authorization and DelegatedPermissionGrant.ReadWrite.All (Microsoft 365); admin.directory.user.security (Google Workspace) |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | AvailableScans run from the TotalHeal cloud against the providers’ APIs. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Essential, Professional or Elite.
Priced per user per year. Counted: member users of the connected Microsoft 365 and Google Workspace tenants.
| Feature | EssentialUS$12per user per year | ProfessionalUS$24per user per year | EliteUS$36per user per year |
|---|---|---|---|
| Microsoft 365 / Entra ID and Google Workspace checks, read-only: MFA and 2-step verification, administrators, legacy authentication, consent, guests, tenant creation, SharePoint and OneDrive sharing | |||
| Score per tenant, findings with the fix, MITRE ATT&CK and compliance controls; accept a risk with a reason and an end date | |||
| Third-party app inventory: apps people granted access, their scopes, who holds them, high-risk access flagged | |||
| Drift alerts: a critical or high setting that starts failing raises an alert in the incident queue | |||
| Fixes TotalHeal applies after a second person approves: stop user consent, restrict guest invitations, revoke an app |
List prices per user per year; minimum 25 users. Each tier includes everything in the tier before it. Volume, multi-product and partner pricing on request.
SaaSPosture is sold on its own, outside the editions.
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- A Microsoft Entra ID / Microsoft 365 or Google Workspace connector in TotalHeal with the read permissions above
- For fixes (Elite): the write permissions above, granted to the same app registration or service account
Procurement documents for SaaSPosture SSPM
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
Get a quote for SaaSPosture SSPM.
Tell us how many users you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.