TotalHealVulnSightVulnerability Management
Know which installed software carries a known, exploited vulnerability — without a scanner appliance.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate VulnSight Vulnerability Management. No card.
Teams cannot patch everything. They need to know which installed software on which device carries a known vulnerability, which are actually being exploited, and which open a path to their most important systems — without deploying a scanner appliance or handing out admin credentials.
Agentless matching on the TotalHeal server: the software inventory the TotalHeal agent already reports is matched against a mirrored vulnerability knowledge base. Nothing extra runs on the endpoint and no scanning credentials are stored.

VulnSight Vulnerability Management, feature by feature.
Linux distro advisories
Debian, Ubuntu (including Ubuntu Pro ESM fixes), Alpine, Red Hat, AlmaLinux and Rocky Linux packages matched against distro advisories.
Windows, macOS and desktop apps
OS builds and about 98 curated desktop applications matched against NVD data. Unmapped apps are reported as “not assessed”, never guessed.
Confidence on every finding
Confirmed, likely or possible — “possible” is shown apart and never counted.
An explained 0–100 risk score
CVSS, CISA KEV (including ransomware use), public exploits, FIRST EPSS, internet exposure, live alerts naming the CVE and asset criticality.
Explore and graph
CVE explorer, per-device view, CVE detail and a graph from device to software to CVE to ATT&CK technique.
Risk acceptance with a second person
Exceptions need a reason and an expiry of at most 365 days, are approved by a different person, revocable and audited.
From finding to fix
“Create patch task” raises an update request through UEM — nothing changes automatically. Findings resolve by themselves when no longer matched.
Exposure management (Enterprise)
Asset exposure score, attack surface, attack paths to crown jewels, crown-jewel tagging and a remediation queue.
How VulnSight Vulnerability Management works.
VulnSight matches the software inventory TotalHeal agents already report against a mirrored vulnerability knowledge base. Every finding has a confidence level and an explained 0–100 risk score built from exploitation evidence, so teams fix what attackers use — without a scanner appliance or stored credentials.
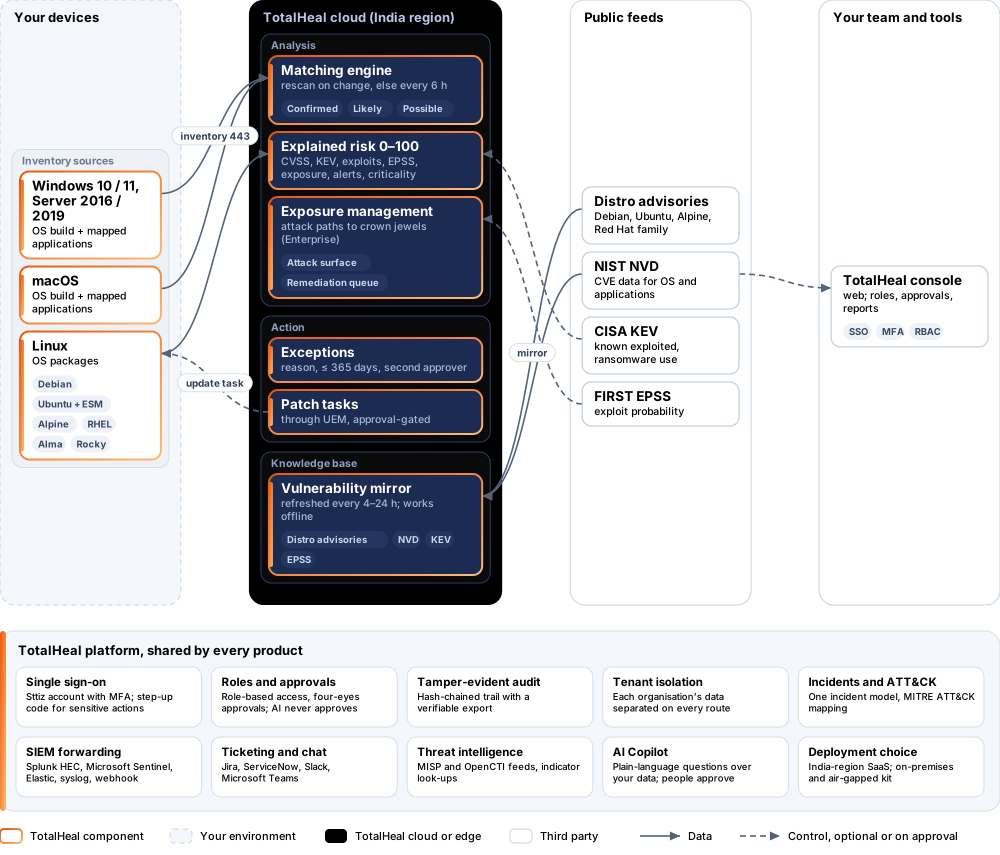
- InventoryAgents report installed OS packages and applications.
- MatchSoftware is matched to distro advisories and NVD data, with a confidence level.
- RankAn explained 0–100 risk from CVSS, KEV, exploits, EPSS, exposure, live alerts and asset criticality.
- ActCreate a patch task through UEM, or accept the risk with a second person’s approval.
- CloseFindings resolve on their own when no longer matched.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Linux: Debian, Ubuntu, Alpine, RHEL, AlmaLinux, Rocky | OS packages |
| Windows 10/11, Windows Server 2016/2019 | OS build and mapped applications |
| macOS | OS build and mapped applications |
| iOS, Android, network devices, containers, language packages | Not assessed |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | Available |
| On-premises | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableThe vulnerability feeds and the control plane run offline. |
Unit and tiers.
Priced per asset per year. Counted: devices reporting a software inventory. List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| CVE matching, confidence, explained risk, KEV / EPSS / CVSS | Included | Included |
| CVE explorer, device view, graph, data sources | Included | Included |
| Exceptions with second-person approval | Included | Included |
| Patch task through UEM | Included (needs UEM) | Included (needs UEM) |
| Exposure score, attack surface, attack paths, crown jewels, remediation queue | — | Included |
| Price | Contact sales | Contact sales |
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- A software-inventory source: today the TotalHeal agent (desktop or Linux server) with its UEM module enabled
- Recommended: Patch Management to act on findings
- A Sttiz account for each console user
Procurement documents for VulnSight Vulnerability Management
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
Part of TotalHeal Endpoint Operations suite and of Complete — each product is still licensed on its own.
TotalHealPatchPilot
Patch Management
See what is missing on every computer and roll updates out in waves — with proof afterwards.
TotalHealDeviceSphere
Unified Endpoint Management (UEM)
Enrol, configure, update and secure every laptop, phone and tablet from one console.
TotalHealWebShield
Web Application Firewall (WAF)
A web application firewall in front of your portals, tuned without breaking real users.
Get a quote for VulnSight Vulnerability Management.
Tell us how many assets you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.