TotalHealIdentityWatchIdentity Threat Detection & Response (ITDR)
Spot identity attacks in your sign-in data and act on them.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate IdentityWatch ITDR. No card.
Most intrusions now start with a valid sign-in: a sprayed password, a tired user approving the tenth MFA push, a malicious app granted access to mail. Identity providers record all of it, but few teams watch it.
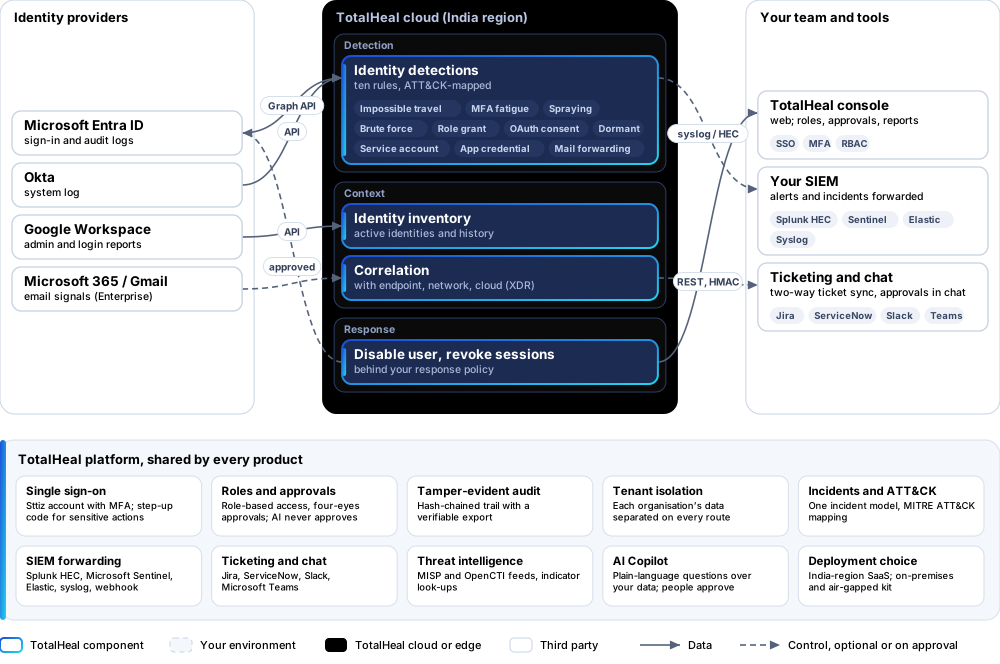
IdentityWatch connects to your identity provider, keeps an inventory of active identities, detects identity attacks in the sign-in and audit data, and lets you disable a user or revoke sessions from the incident.
IdentityWatch ITDR, feature by feature.
Identity provider connector
Microsoft Entra ID, Okta or Google Workspace sign-in and audit logs, read through the provider’s API.
Ten identity detections
Impossible travel, MFA fatigue, password spraying, brute force on one account, privileged role grants, suspicious OAuth consent, dormant-account sign-in, interactive sign-in by a service account, new application credentials and mailbox forwarding to an outside address — each mapped to MITRE ATT&CK.
Identity inventory
Every active identity seen, with its sign-in history and alerts.
Response
Disable a user or revoke their sessions, behind your response policy and its approvals.
One incident
Identity alerts join the same incidents as endpoint, network and cloud alerts when ThreatFusion XDR is present.
Email signals (Enterprise)
Microsoft 365 and Google Workspace email signals for your users — the providers’ own verdicts.
How IdentityWatch ITDR works.
IdentityWatch reads your identity provider’s sign-in and audit logs, detects ten identity attack patterns — from password spraying to malicious OAuth consent — and lets you disable a user or revoke sessions from the incident.
- ConnectGrant read access to the identity provider’s logs.
- WatchEvery active identity and its sign-ins.
- DetectSpraying, MFA fatigue, impossible travel, risky consent and more.
- RespondDisable or revoke sessions behind your approval rules.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Identity providers | Microsoft Entra ID, Okta, Google Workspace |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | AvailableSingle-region service. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Unit and tiers.
Priced per identity per year. Counted: active identities seen through the connector. List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| Connector, identity detections, inventory, response | Included | Included |
| Microsoft 365 and Google Workspace email signals | — | Included |
| Price | Contact sales | Contact sales |
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- An administrator who can grant TotalHeal read access to the identity provider’s logs
Procurement documents for IdentityWatch ITDR
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
TotalHealThreatFusion
Extended Detection & Response (XDR)
One incident across endpoint, network, identity, email and cloud — with or without our EDR.
TotalHealZeroGate
Zero Trust Network Access (ZTNA)
Access to named apps and servers only, re-checked continuously — not the whole subnet.
Get a quote for IdentityWatch ITDR.
Tell us how many identitys you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.