TotalHealInfraGuardServer & Infrastructure Security (hardening and configuration)
Continuously checks how your Linux servers are configured — 79 hardening checks with evidence — and fixes them with a second person’s approval and a rollback for every change.
Trial: 30 days, up to 5 servers. You sign in to the TotalHeal console with a Sttiz account and activate InfraGuard Server Hardening. No card.
Most server breaches start with a setting, not a zero-day: root logins over SSH, password logins open to the internet, weak ciphers, world-readable shadow files, no audit trail, no firewall. Servers drift — a hardened image is weakened by the next change — and auditors ask for evidence that nobody has.
InfraGuard runs a 79-check hardening benchmark on every Linux server through the TotalHeal server agent, scores each server and the fleet, alerts when a check newly fails, and fixes what you approve — with a backup, a check that the fix took effect, and a rollback for every change.

InfraGuard Server Hardening, feature by feature.
79 checks with evidence
SSH (root and password login, attempts, ciphers, MACs, key exchange, host keys), kernel and network settings, accounts and PAM, file permissions, services, logging and audit, updates, firewall, time sync, SELinux / AppArmor, Secure Boot and Docker — each result with the exact value found.
Why it matters, how to fix
Every check explains the risk in one sentence and names its fix or the guidance to follow.
Score per server and for the fleet
A severity-weighted score from 0 to 100 (critical 10, high 6, medium 3, low 1), score history, and the checks failing on most servers.
Drift alerts
A check that newly fails at critical or high raises an alert (MITRE ATT&CK T1562.001) in the same incident queue as every other alert.
Fixes with four-eyes approval
Request a fix with a reason; a second person approves — never the requester, never an AI; the agent applies it as a signed command.
Backup, verify, roll back
Every file a fix touches is backed up first; the host is re-read to check the fix took effect, and a fix that did not is rolled back automatically. Any applied fix can be rolled back later, byte for byte.
Safe where it matters
SSH changes are validated with sshd -t before reload; firewall and partition changes are guidance only, never automatic; remediation runs only where the host owner allowed it.
Accepted risks
An exception for one server or all servers needs a reason, an expiry of up to a year and a second person; it leaves the score while it lasts.
Evidence by control
Results grouped by ISO 27001:2022 Annex A control and the CERT-In directions (log retention, clock synchronisation) for auditors.
On the host too
totalheal-server-agent infraguard scan | fix | rollback runs the same benchmark on a server without the cloud.
How InfraGuard Server Hardening works.
InfraGuard checks every Linux server against 79 hardening checks, shows the exact setting it found, alerts the moment a server drifts, and fixes what a second person approves — backing up every file, checking each fix took effect and keeping a rollback for every change.
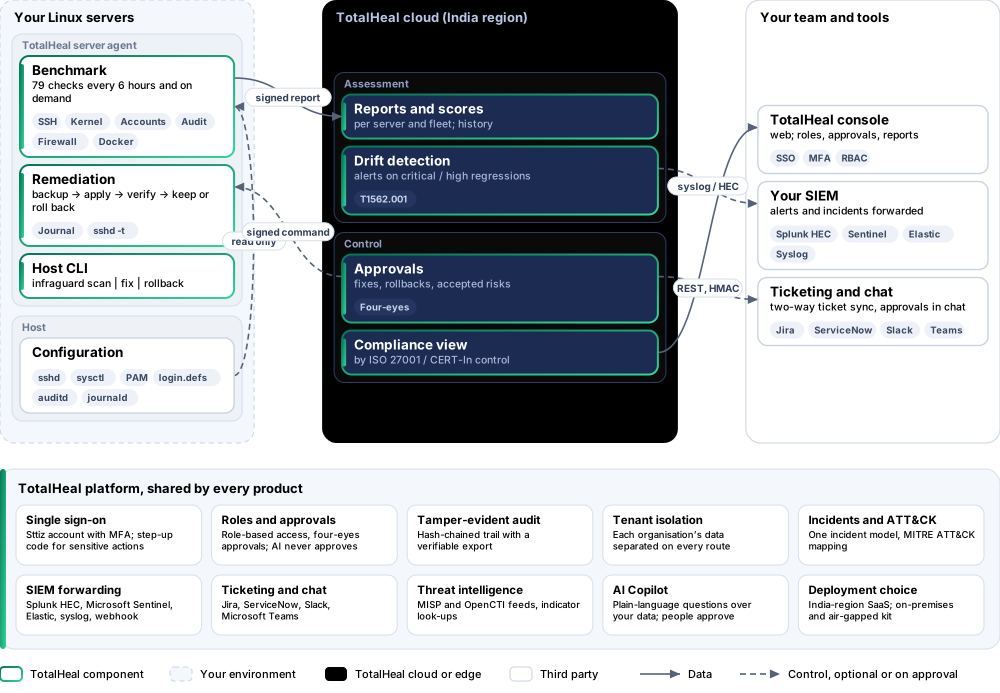
- ScanThe server agent reads the host — files, kernel settings, services — every 6 hours and on demand; nothing is changed.
- ScoreEach check passes or fails with evidence; a severity-weighted score per server and for the fleet.
- AlertA check that newly fails at critical or high raises an alert in the incident queue.
- ApproveSomeone requests a fix with a reason; a different person approves it.
- Fix and verifyThe agent backs up, applies, re-reads the host and rolls back any fix that did not take effect.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Ubuntu 20.04, 22.04, 24.04 | TotalHeal server agent (signed .deb) |
| Debian 11, 12 | TotalHeal server agent (signed .deb) |
| RHEL, Rocky Linux, AlmaLinux 8 and 9 | TotalHeal server agent (signed .rpm) |
| Docker hosts | Socket permissions, TCP exposure and inter-container traffic checked |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | AvailableSingle-region service. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Unit and tiers.
Priced per server per year. Counted: servers reporting the InfraGuard benchmark. List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| Benchmark, scores, drift alerts, approved fixes with rollback, exceptions, compliance view, host CLI | Included | Included |
| Price | Contact sales | Contact sales |
InfraGuard is sold on its own, outside the editions.
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- The TotalHeal server agent on each Linux server, with infraguard.enabled
- infraguard.allow_remediation on servers where approved fixes may run
- Outbound HTTPS from each server to the TotalHeal cloud
Procurement documents for InfraGuard Server Hardening
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
Get a quote for InfraGuard Server Hardening.
Tell us how many servers you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.