TotalHealRecoveryVaultBackup & Cyber Recovery
Encrypted, incremental backup of Linux servers and their databases, with verified restore points and ransomware detection in every backup.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate RecoveryVault Backup & Cyber Recovery. No card.
Ransomware now goes after backups first: it deletes them, encrypts them or waits until the bad files are in every copy. Many organisations find out during the incident that their last good backup is weeks old, unreadable or reachable with the same stolen administrator password.
RecoveryVault encrypts on the server before anything leaves it, keeps incremental, deduplicated restore points on your storage or ours, scores every backup for ransomware, and restores only through approved, audited jobs.
RecoveryVault Backup & Cyber Recovery, feature by feature.
Encrypted before it leaves
AES-256-GCM on the server with keys derived from that server’s own root key. Storage and TotalHeal see only ciphertext, and every stored object is bound to its identity, so a swapped object is refused.
Incremental and deduplicated
Content-defined chunking sends only what changed: one edit inside a 6 MiB file uploaded less than 3 MiB in our end-to-end test. Identical blocks are stored once.
Databases, natively
PostgreSQL and MySQL dumped by their own tools inside the backup run, with pre- and post-backup scripts for anything else that must be quiesced.
Schedules, windows and retention
Per-policy schedules and backup windows, and grandfather-father-son retention: daily, weekly, monthly and yearly points kept as long as you set.
Your storage or ours
TotalHeal storage, or your own S3-compatible bucket (AWS S3, MinIO, Wasabi or a NAS with an S3 interface). Backup data goes straight from the server to storage.
Ransomware score on every backup
Change ratio, entropy jumps on normally compressible files, new extensions and deletions give a 0–100 score. At your threshold the point is marked suspect, an incident opens and the last good point is held.
Restores that never destroy data
Restore to the same server, a folder or another server. Files are written through temporary copies, verified against their checksum, and replaced files are moved aside, never deleted.
Four-eyes recovery
Restores to another server and rollbacks wait for a second person; the requester can never approve their own job. Every key release and job is in the tamper-evident audit.
Verification
Scheduled and on-demand verification jobs read restore points back and check them, so a backup is known to be restorable before it is needed.
A lost server can be rebuilt
Each server’s root key is escrowed sealed, and released only to the same server or to the agent running an approved restore job, sealed to that job’s one-time key.
How RecoveryVault Backup & Cyber Recovery works.
RecoveryVault treats the backup as the target it now is. Data is encrypted on the server before it leaves, every restore point is scored for ransomware as it is taken, and nothing is restored to another place without a second person. The result is a restore point you can trust on the worst day, not only a copy of the files.
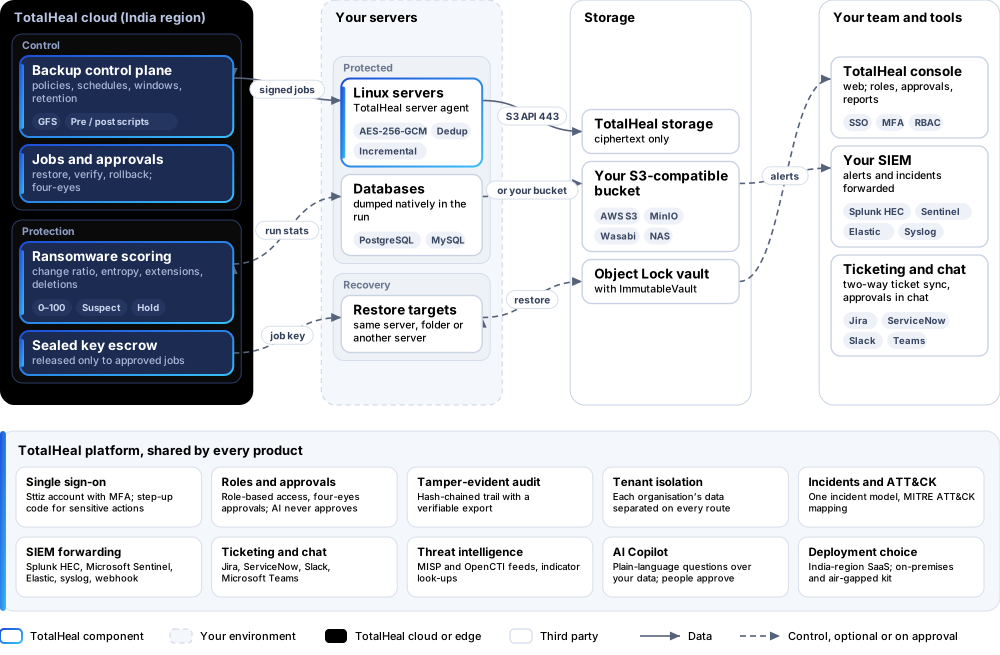
- ProtectSwitch backup on for a server and attach a policy: what to back up, databases, schedule, window and retention.
- Back upThe agent chunks changed data, encrypts it and uploads it straight to storage; the restore point is committed only when every object is confirmed.
- ScoreEach run is scored 0–100 for ransomware; a suspect point opens an incident and the last good point is held.
- VerifyVerification jobs read restore points back on a schedule, so you know they restore before you need them.
- RestorePick a point and a target; restores to another server wait for a second person, and nothing on the target is deleted.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Linux servers: Debian, Ubuntu, RHEL, AlmaLinux, Rocky | TotalHeal server agent (signed .deb and .rpm packages) |
| Databases | PostgreSQL and MySQL, dumped natively |
| Storage | TotalHeal storage, or any S3-compatible bucket: AWS S3, MinIO, Wasabi, S3-capable NAS |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS control plane (India region) with TotalHeal storage | AvailableSingle-region service. |
| SaaS control plane with your own S3 storage | AvailableBackup data goes from your servers straight to your bucket. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableWith storage inside your network. |
Unit and tiers.
Priced per protected terabyte per year. Counted: data selected for backup, in terabytes; the counting rule is set in the quote until list prices are published. List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| Encrypted incremental backup, databases, schedules, retention, ransomware score, restores, four-eyes approval, verification, audit | Included | Included |
| Immutable copies (ImmutableVault), clean recovery (CyberRecover), DR plans and drills (DisasterRecover) | Separate products | Separate products |
| Price | Contact sales | Contact sales |
RecoveryVault is sold on its own, outside the editions; there is no Business/Enterprise split.
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- The TotalHeal server agent on each Linux server, with backup switched on
- Storage: TotalHeal’s, or an S3-compatible bucket you own
- Outbound HTTPS from each server to the TotalHeal cloud and to the storage
Procurement documents for RecoveryVault Backup & Cyber Recovery
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
Get a quote for RecoveryVault Backup & Cyber Recovery.
Tell us how many protected terabytes you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.