
One platform. Your environment.
40 products — 39 of them available today — and 5 platform capabilities run on one platform: one console, one sign-in, one audit trail and one agent on each device. Shared capabilities come with every product, scoped to what you own; they are never sold on their own.
Platform
Included with your products.
Each capability works on the data your own products collect. A compliance view, for example, only evaluates controls your products give evidence for, and says plainly what is not covered.
TotalHealSOC Center
Security Operations Command Center
The SOC Command Center: posture, incidents, alerts, threat map, attack-surface coverage and MITRE ATT&CK activity on one screen.
TotalHealVideo Wall
SOC Visualisation
SOC views on a wall of screens: layouts, schedules, paired displays and a full-screen wall for an operations room. Live in the console.
More about Video WallTotalHealAI Copilot
Security AI Assistant
An assistant in the console that answers questions about your own data, explains alerts and drafts actions. Destructive actions always need a human; AI never approves.
TotalHealHuntSphere
Endpoint Threat Hunting
Threat hunting in the console: search across the events your products collect, with saved hunts.
TotalHealAssetDiscover
Asset Discovery & Inventory
One inventory of enrolled devices and their software, part of DeviceSphere UEM, VulnSight and ThreatTrace. Network discovery of devices without an agent is coming; it does not exist yet.
Incident Management
Incidents with timelines, assignees and status, shared by every product that raises alerts.
Threat Intelligence
Reputation look-ups for domains, IPs and files inside the products that use them. Not sold as a separate threat-intelligence platform.
Compliance & Reporting
Reports and a hash-chained audit trail. Compliance views evaluate only the controls your products give evidence for, and say honestly what is not covered.
See the whole picture on one screen.
The SOC Command Center brings security posture, active incidents, alerts, endpoints at risk, a threat map, attack-surface coverage, alerts by severity and MITRE ATT&CK activity together. What it shows depends on the products you own.
See which products feed it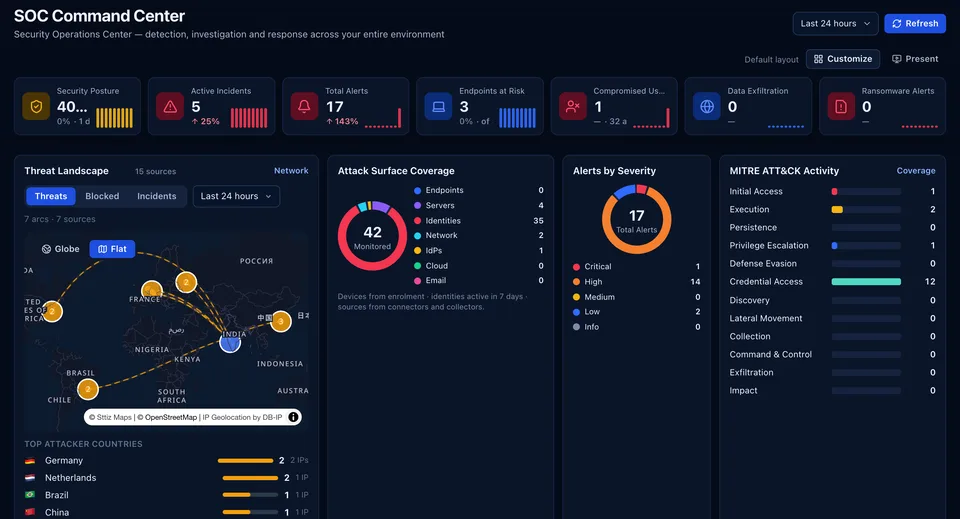
Bring the tools you already run.
41 connectors available in the console today. Each is set up from a card with a test button: API connectors use read-only credentials, sealed on our side; the others send their logs to the TotalHeal collector. A connector comes with the products that use its data.
Works with
41 integrations
 Supported
FortiGate
Fortinet · Syslog
Firewall logs over syslog; scans, denied-connection bursts, brute force and threat-intel hits raise alerts.
 Supported
PAN-OS
Palo Alto Networks · Syslog
Firewall logs over syslog; scans, denied-connection bursts, brute force and threat-intel hits raise alerts.
 Supported
ASA and Firepower Threat Defense
Cisco · Syslog
Firewall logs over syslog; scans, denied-connection bursts, brute force and threat-intel hits raise alerts.
 Supported
Sophos Firewall (XG / XGS)
Sophos · Syslog
Firewall logs over syslog; scans, denied-connection bursts, brute force and threat-intel hits raise alerts.
 Supported
Log Exporter or CEF
Check Point · Syslog
Firewall logs over syslog; scans, denied-connection bursts, brute force and threat-intel hits raise alerts.
 Supported
pfSense
Netgate · Syslog
Firewall logs over syslog; scans, denied-connection bursts, brute force and threat-intel hits raise alerts.
 Supported
OPNsense
Deciso · Syslog
Firewall logs over syslog; scans, denied-connection bursts, brute force and threat-intel hits raise alerts.
 Supported
Defender for Endpoint
Microsoft · API
Pulls the vendor's alerts; each becomes one TotalHeal alert with its ATT&CK technique.
 Supported
Falcon
CrowdStrike · API
Pulls the vendor's alerts; each becomes one TotalHeal alert with its ATT&CK technique.
 Supported
Singularity
SentinelOne · API
Pulls the vendor's alerts; each becomes one TotalHeal alert with its ATT&CK technique.
- Supported
Sophos Central
Sophos · API
Pulls the vendor's alerts; each becomes one TotalHeal alert with its ATT&CK technique.
- Supported
Entra ID
Microsoft · API
Reads sign-in and audit logs through Microsoft Graph.
 Supported
Okta
Okta · API
Reads the Okta System Log.
 Supported
Google Workspace
Google · API
Reads Workspace sign-in and admin activity.
- Supported
Active Directory and Windows
Microsoft · Collector
Windows security events (sign-ins, account and group changes, lockouts) through NXLog or Winlogbeat.
 Supported
AWS CloudTrail
Amazon Web Services · API
Reads CloudTrail through the API, or from S3 through SQS.
 Supported
Azure Activity Log
Microsoft · API
Reads subscription activity through the Azure API.
 Supported
Google Cloud Audit Logs
Google · API
Reads Cloud Audit Logs.
- Supported
Microsoft 365 unified audit log
Microsoft · API
Reads tenant-wide Microsoft 365 activity.
- Supported
Microsoft 365 message trace
Microsoft · API
Reads mail flow through Microsoft Graph.
- Supported
Defender for Office 365
Microsoft · API
Pulls email threat alerts through Microsoft Graph.
 Supported
Zeek
Zeek · Collector
Reads conn, http, ssl, ssh, files and notice logs.
 Supported
Suricata
OISF · Collector
Reads EVE JSON alerts, with ATT&CK taken from the rule metadata.
- Supported
DNS query logs (BIND, Zeek)
Open standard · Collector
Threat-intel domains and random-looking new domains raise alerts.
 Supported
MISP
MISP Project · API
Imports indicators and events from your MISP.
 Supported
OpenCTI
Filigran · API
Imports indicators, threat actors and campaigns.
- Supported
STIX / TAXII 2.1
Open standard · API
Polls TAXII 2.1 collections for indicators.
 Supported
Jira
Atlassian · API
Opens incident tickets and keeps them in sync both ways.
 Supported
ServiceNow
ServiceNow · API
Opens incident tickets and keeps them in sync both ways.
 Supported
Slack
Slack · API
Posts alerts and incident updates to a channel.
 Supported
Microsoft Teams
Microsoft · API
Posts alerts and incident updates to a channel.
 Supported
Splunk
Splunk · Forwarding
Forwards events and alerts to your Splunk.
- Supported
Microsoft Sentinel
Microsoft · Forwarding
Forwards events and alerts to your Sentinel workspace.
 Supported
Elastic
Elastic · Forwarding
Forwards events and alerts to your Elasticsearch.
- Supported
Syslog or CEF out
Open standard · Forwarding
Forwards events as syslog or CEF to any other SIEM.
- Supported
Signed webhooks out
Open standard · Webhook
Sends signed webhooks to your own tools.
- Supported
Syslog (RFC 3164 / 5424)
Open standard · Collector
Any device or app that speaks syslog.
- Supported
CEF and LEEF
Open standard · Collector
Any product that emits CEF or LEEF.
- Supported
JSON, CSV and files
Open standard · Collector
Files and JSON or CSV feeds from your own apps.
- Supported
Signed webhooks in
Open standard · Webhook
Your tools push events to a signed, per-source address.
 Supported
OpenTelemetry logs
CNCF · Collector
OTLP/HTTP logs (JSON) through the collector.
“Supported” means the connector is in the console today, set up from a card with a test button; the chips show the status of the TotalHeal products that use it. Product names and logos are trademarks of their respective owners. Their use does not imply endorsement or partnership. Credits: AWS logo, Apache License 2.0; MISP logo by the MISP Project, CC BY 4.0; OpenTelemetry logo, CC BY 4.0.
TotalHeal AssetDiscover inventories enrolled devices today; network discovery of devices without an agent is coming. The SOC Center, Video Wall, AI Copilot and HuntSphere are included with the security-operations products you own and are not sold on their own.