TotalHealResponseFlowSOAR & Automation
Automate response with playbooks — and keep a person in the loop.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate ResponseFlow SOAR. No card.
Alerts from many tools arrive faster than a team can open tickets, enrich them and act, and automation that acts on its own is a risk of its own.
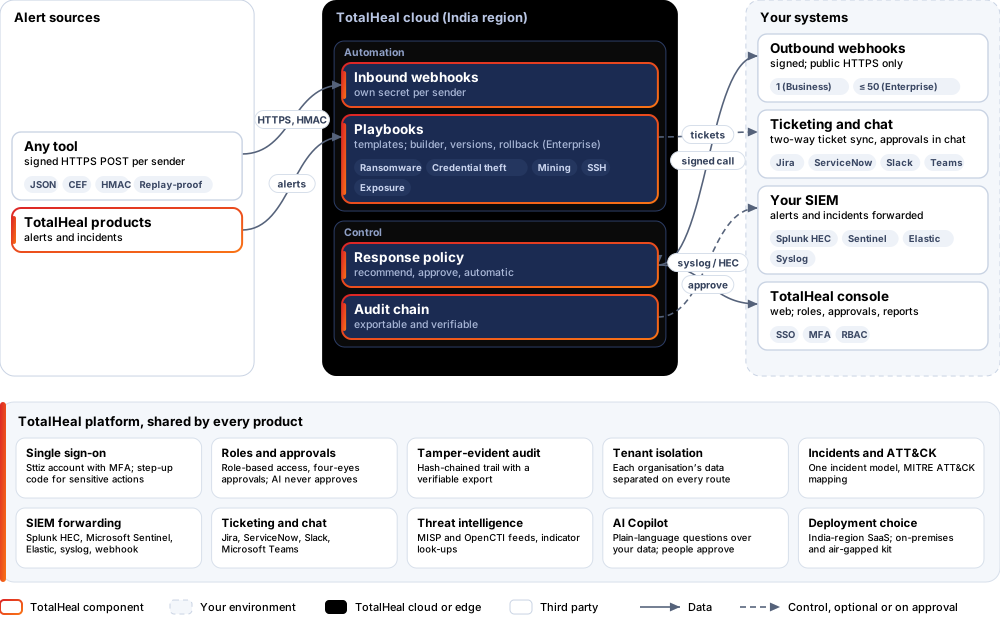
ResponseFlow takes alerts from its own signed webhook or from other TotalHeal products and runs playbooks on them. Every action goes through your response policy and its approvals, and every step is on a tamper-evident audit chain.
ResponseFlow SOAR, feature by feature.
Its own alert source
A signed inbound webhook per sending tool (JSON or CEF), each with its own secret; replays and old timestamps are refused. No SIEM or XDR licence is needed.
Template playbooks
Ready playbooks for third-party alerts, ransomware, credential theft, crypto-mining, SSH compromise and exposures. On Business you set their parameters — severities, risk threshold, messages, case titles and the webhook they call.
Custom playbooks (Enterprise)
Build your own playbooks with conditions, versions and rollback.
A person approves
Actions follow the response policy: recommend, approve or automatic; high-impact actions such as webhooks and isolation always wait for approval.
Signed outbound webhooks
Calls to your ticketing or chat tool are signed and leave only to public HTTPS addresses. Business includes one endpoint; Enterprise up to 50.
Audit you can verify
Every request, approval and result is on a hash-chained audit log that can be exported and verified.
How ResponseFlow SOAR works.
ResponseFlow takes alerts from its own signed webhook or from other TotalHeal products and runs playbooks on them. Every action follows your response policy and approvals, and every step is on a tamper-evident audit chain — automation that does not act behind your back.
- ReceiveA signed alert arrives; replays and old timestamps are refused.
- MatchA playbook matches on severity, type and your parameters.
- ApproveHigh-impact actions wait for a person.
- ActOpen a ticket, post to chat, isolate or notify.
- RecordRequest, approval and result on the audit chain.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Senders | Any tool that can send an HTTPS POST with an HMAC signature |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | AvailableSingle-region service. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Unit and tiers.
Priced per analyst per year. Counted: people who run or approve playbooks. List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| Inbound alert webhooks, template playbooks with parameters, approvals, audit | Included | Included |
| Outbound webhook endpoints | 1 | Up to 50 |
| Custom playbooks, builder, versions and rollback | — | Included |
| Price | Contact sales | Contact sales |
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- An alert source: a tool that can send signed HTTPS requests, or other TotalHeal products
Procurement documents for ResponseFlow SOAR
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
Part of TotalHeal Security Operations suite and of Complete — each product is still licensed on its own.
TotalHealLogIntelligence
SIEM & Log Management
Collect, search and alert on logs from firewalls, DNS servers, servers and identity providers.
TotalHealThreatFusion
Extended Detection & Response (XDR)
One incident across endpoint, network, identity, email and cloud — with or without our EDR.
Get a quote for ResponseFlow SOAR.
Tell us how many analysts you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.