TotalHealLogIntelligenceSIEM & Log Management
Collect, search and alert on logs from firewalls, DNS servers, servers and identity providers.
Trial: 30 days. You sign in to the TotalHeal console with a Sttiz account and activate LogIntelligence SIEM. No card.
Firewalls, DNS servers and servers write the evidence of most attacks into logs nobody reads until after an incident — and SIEM licences often punish you for sending more of them.
A collector at your site sends syslog, CEF and log files to TotalHeal, where they are parsed, searched and checked by built-in detection rules. Ingest is metered per day, and nothing is ever dropped because of the licence.
LogIntelligence SIEM, feature by feature.
Collector at your site
Syslog over UDP, TCP or TLS, CEF, JSON and log files, from one enrolled collector with its own device identity. If the cloud is unreachable it keeps the events on disk and sends them later.
Parsers for common sources
FortiGate, pfSense / OPNsense, CEF firewalls (Check Point, Palo Alto), BIND and Zeek DNS logs, SSH logs, Microsoft Entra ID, Okta, Google Workspace, Microsoft 365, AWS CloudTrail, Azure Activity and Google Cloud audit logs.
Detection rules for network logs
Port scans and host sweeps, bursts of denied connections, allowed connections to threat-intelligence addresses, DNS queries for threat-intelligence domains, newly seen algorithm-like domains and login brute force from one address — each mapped to MITRE ATT&CK.
Search, saved searches and scheduled rules
One query language over every source; save searches and schedule them as rules that raise alerts. Business includes up to 10 scheduled rules, each run at most every 15 minutes.
Metered ingest that never drops data
Accepted volume is measured per source and day. At 100 % of your licence you are alerted; up to 150 % the extra is billed; above that only sources that were not sending yet wait in their collector — existing sources keep sending.
Retention you can see
Events are kept 180 days by default, the CERT-In minimum; the retention view shows the setting, the floor and any approved change.
Measured on our test system
In our 25 Oct 2026 run, one collector took 30,000 FortiGate traffic lines over syslog/TCP into a test service on a development machine in 23 seconds (about 1,300 events a second), metered at 670 bytes per event, so 1 GB a day is about 1.5 million such lines; a search over them answered in 124–145 ms. The port scan and the burst of denied connections in the replay each raised one alert.
How LogIntelligence SIEM works.
LogIntelligence collects syslog, CEF, JSON and log files through a collector at your site, parses common firewalls, DNS, identity and cloud sources, and alerts on built-in detection rules. Ingest is metered per day; above the licence you are alerted and billed, never silently dropped.
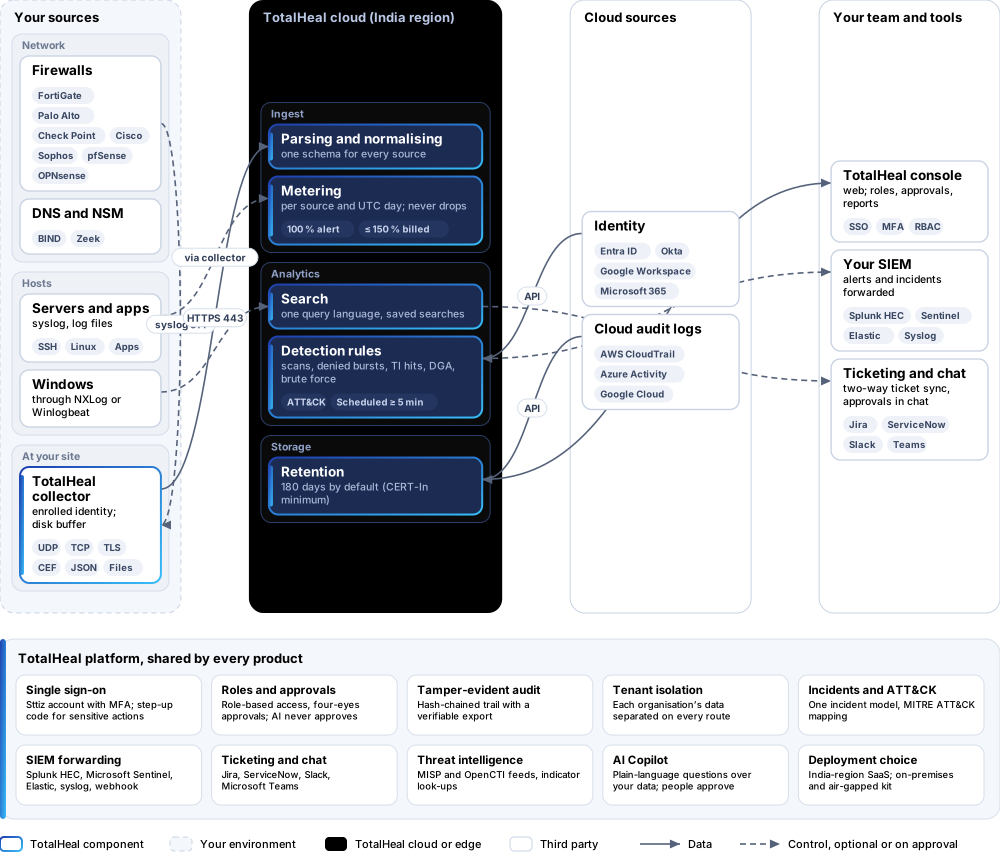
- CollectEnrol a collector; point syslog, CEF, JSON and log files at it.
- ParseBuilt-in parsers normalise common sources into one schema.
- DetectBuilt-in rules for scans, denied bursts, threat-intel hits and brute force raise alerts.
- SearchOne query language, saved searches and scheduled rules.
- Keep180 days by default, with the retention view showing settings and approved changes.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Collector | Linux with systemd, x86_64 or aarch64 (.deb / .rpm packages through our team until the public package repository opens) |
| Sources | Anything that sends syslog, CEF or JSON, or writes log files; Windows events through NXLog or Winlogbeat |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) with a collector at your site | AvailableSingle-region service; no archive tier yet. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Unit and tiers.
Priced per gb of log ingest per day. Counted: accepted bytes per UTC day (normalised events). List prices are not published yet — our team quotes per unit and term.
| Business | Enterprise | |
|---|---|---|
| Collector, parsers, search, saved searches, retention view | Included | Included |
| Built-in detection rules for firewall and DNS logs | Included | Included |
| Scheduled rules | Up to 10, every 15 min or more | Unlimited, every 5 min or more |
| Hunt packs, correlation studio, detection engineering | — | Included |
| Price | Contact sales | Contact sales |
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- A Linux host at your site for the collector, reachable by your log sources
- Outbound HTTPS from the collector to TotalHeal
Procurement documents for LogIntelligence SIEM
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Works well with
Part of TotalHeal Security Operations suite and of Complete — each product is still licensed on its own.
TotalHealThreatFusion
Extended Detection & Response (XDR)
One incident across endpoint, network, identity, email and cloud — with or without our EDR.
TotalHealResponseFlow
SOAR & Automation
Automate response with playbooks — and keep a person in the loop.
TotalHealDNSGuard
DNS Firewall & Security
Stop malware, phishing and DNS tunnelling at the lookup — for every device, on site or on the road.
Get a quote for LogIntelligence SIEM.
Tell us how many gb of log ingests you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.