SIEM & Log Management
A SIEM that never drops your logs because of the licence
Collect, search and alert on logs from firewalls, DNS servers, servers and identity providers.
Contents
- 1Executive summary
- 2The challenge
- 3Architecture
- 4How it works
- 5Capabilities in detail
- 6Security and data handling
- 7Where it fits
- 8Deployment and system requirements
- 9Technical specifications
- 10Getting started
1Executive summary
LogIntelligence collects syslog, CEF, JSON and log files through a collector at your site, parses common firewalls, DNS, identity and cloud sources, and alerts on built-in detection rules. Ingest is metered per day; above the licence you are alerted and billed, never silently dropped.
2The challenge
Firewalls, DNS servers and servers write the evidence of most attacks into logs nobody reads until after an incident — and SIEM licences often punish you for sending more of them.
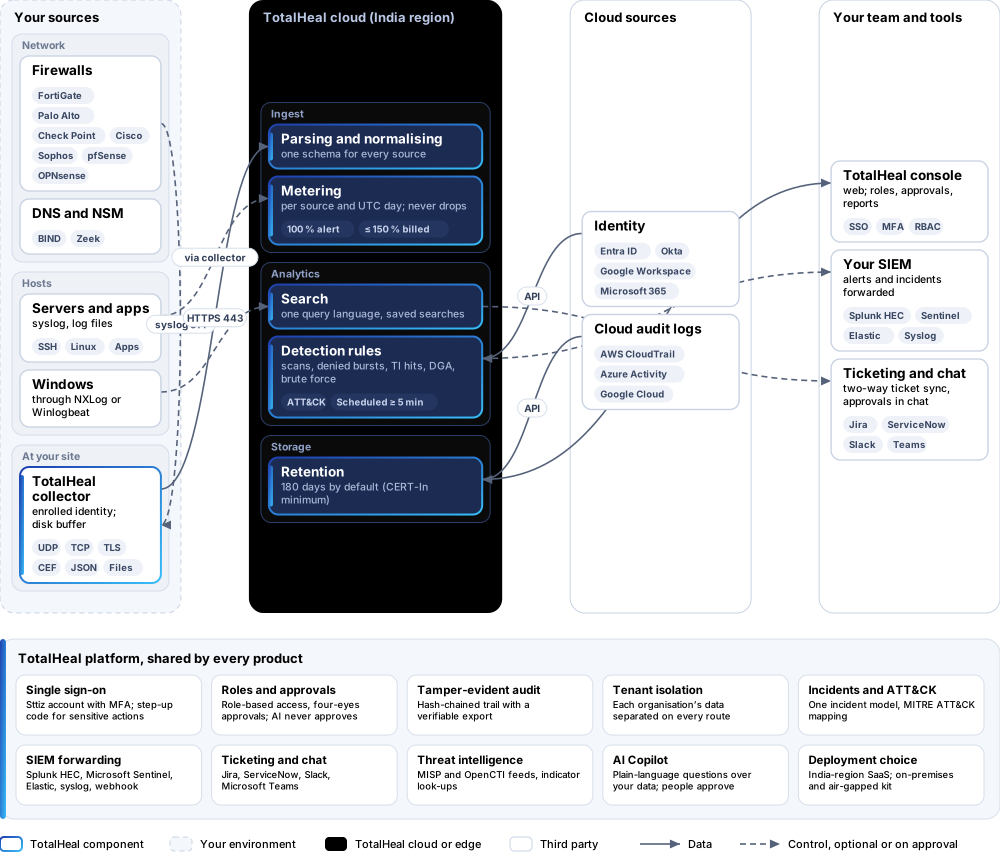
The TotalHeal approach. A collector at your site sends syslog, CEF and log files to TotalHeal, where they are parsed, searched and checked by built-in detection rules. Ingest is metered per day, and nothing is ever dropped because of the licence.
3Architecture
4How it works
- CollectEnrol a collector; point syslog, CEF, JSON and log files at it.
- ParseBuilt-in parsers normalise common sources into one schema.
- DetectBuilt-in rules for scans, denied bursts, threat-intel hits and brute force raise alerts.
- SearchOne query language, saved searches and scheduled rules.
- Keep180 days by default, with the retention view showing settings and approved changes.
5Capabilities in detail
- Collector at your siteSyslog over UDP, TCP or TLS, CEF, JSON and log files, from one enrolled collector with its own device identity. If the cloud is unreachable it keeps the events on disk and sends them later.
- Parsers for common sourcesFortiGate, pfSense / OPNsense, CEF firewalls (Check Point, Palo Alto), BIND and Zeek DNS logs, SSH logs, Microsoft Entra ID, Okta, Google Workspace, Microsoft 365, AWS CloudTrail, Azure Activity and Google Cloud audit logs.
- Detection rules for network logsPort scans and host sweeps, bursts of denied connections, allowed connections to threat-intelligence addresses, DNS queries for threat-intelligence domains, newly seen algorithm-like domains and login brute force from one address — each mapped to MITRE ATT&CK.
- Search, saved searches and scheduled rulesOne query language over every source; save searches and schedule them as rules that raise alerts. Business includes up to 10 scheduled rules, each run at most every 15 minutes.
- Metered ingest that never drops dataAccepted volume is measured per source and day. At 100 % of your licence you are alerted; up to 150 % the extra is billed; above that only sources that were not sending yet wait in their collector — existing sources keep sending.
- Retention you can seeEvents are kept 180 days by default, the CERT-In minimum; the retention view shows the setting, the floor and any approved change.
- Measured on our test systemIn our 25 Oct 2026 run, one collector took 30,000 FortiGate traffic lines over syslog/TCP into a test service on a development machine in 23 seconds (about 1,300 events a second), metered at 670 bytes per event, so 1 GB a day is about 1.5 million such lines; a search over them answered in 124–145 ms. The port scan and the burst of denied connections in the replay each raised one alert.
6Security and data handling
- Nothing dropped for the licenceAt 100 % you are alerted; up to 150 % is billed; existing sources keep sending.
- Survives outagesThe collector keeps events on disk and sends them later.
- Its own identityEach collector is an enrolled device with its own identity.
7Where it fits
8Deployment and system requirements
Protected platforms
- Collectorx86_64, aarch64, systemd
- FortiGate
- Palo Alto Networks
- Check Point
- Cisco
- Sophos
- pfSense / OPNsense
- Zeek / BIND
Works with
- Microsoft Entra ID
- Okta
- Google Workspace
- Microsoft 365
- AWS
- Microsoft Azure
- Google Cloud
On-premises server
- Operating system
- RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12
- Processor
- 4 vCPU (tested configuration)
- Memory
- 8 GB recommended (6 GB minimum)
- Disk
- 10 GB free for software, releases and backups, plus data
- Sign-in
- Active Directory / LDAP, SAML 2.0 or OpenID Connect
- Software
- Nothing to pre-install: no container runtime, database, web server or Java
Network and access
- A Linux host at your site for the collector, reachable by your log sources
- Outbound HTTPS from the collector to TotalHeal
Alerts and tickets to
- Splunk
- Microsoft Sentinel
- Elastic
- Syslog / CEF
- Jira
- ServiceNow
- Slack
- Microsoft Teams
9Technical specifications
| Features | Included | |
|---|---|---|
| Collector at your site | Included | |
| Parsers for common sources | Included | |
| Detection rules for network logs | Included | |
| Search, saved searches and scheduled rules | Included | |
| Metered ingest that never drops data | Included | |
| Retention you can see | Included | |
| Measured on our test system | Included | |
| Availability by edition | Business | Enterprise |
| Collector, parsers, search, saved searches, retention view | Included | Included |
| Built-in detection rules for firewall and DNS logs | Included | Included |
| Scheduled rules | Up to 10, every 15 min or more | Unlimited, every 5 min or more |
| Hunt packs, correlation studio, detection engineering | — | Included |
| Platforms and coverage | ||
| Collector | Linux with systemd, x86_64 or aarch64 (.deb / .rpm packages through our team until the public package repository opens) | |
| Sources | Anything that sends syslog, CEF or JSON, or writes log files; Windows events through NXLog or Winlogbeat | |
| Console | TotalHeal web console | |
| Deployment options | ||
| SaaS (India region) with a collector at your site | AvailableSingle-region service; no archive tier yet. | |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. | |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. | |
| Licensing | ||
| Priced per | GB of log ingest per day | |
| Counted | Accepted bytes per UTC day (normalised events) | |
| Trial | 30 days | |
| Government profile | Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks. | |
| Procurement dossier | Compliance matrix, bill of materials, architecture and hardening, SLA and OEM authorisation letter, on request | |
| On-premises server | ||
| Operating system | RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12 | |
| Processor | 4 vCPU (tested configuration) | |
| Memory | 8 GB recommended (6 GB minimum) | |
| Disk | 10 GB free for software, releases and backups, plus data | |
| Sign-in | Active Directory / LDAP, SAML 2.0 or OpenID Connect | |
| Software | Nothing to pre-install: no container runtime, database, web server or Java | |
| Requirements | ||
| Requirement 1 | A Linux host at your site for the collector, reachable by your log sources | |
| Requirement 2 | Outbound HTTPS from the collector to TotalHeal | |
10Getting started
- A Linux host at your site for the collector, reachable by your log sources
- Outbound HTTPS from the collector to TotalHeal
Start a 30 days trial in the TotalHeal console with a Sttiz account. For a quote, an on-premises installation or the procurement dossier (compliance matrix, bill of materials, architecture and hardening, SLA, OEM authorisation letter), write to business@totalhealsecurity.com.