TotalHealPromptShieldAI Security (GenAI firewall)
See which AI assistants your people use and block the ones you have not approved; put your own AI applications behind a gateway that stops sensitive data and injection attempts.
Trial: 30 days, up to 50 users. You sign in to the TotalHeal console with a Sttiz account and activate PromptShield AI Security. No card.
People paste contracts, customer records and source code into whichever AI assistant is open, and the company’s own AI applications send whatever their users type straight to a model provider. Nobody can say which assistants are in use, what data has left, or whether someone is trying to talk an internal assistant into ignoring its instructions.
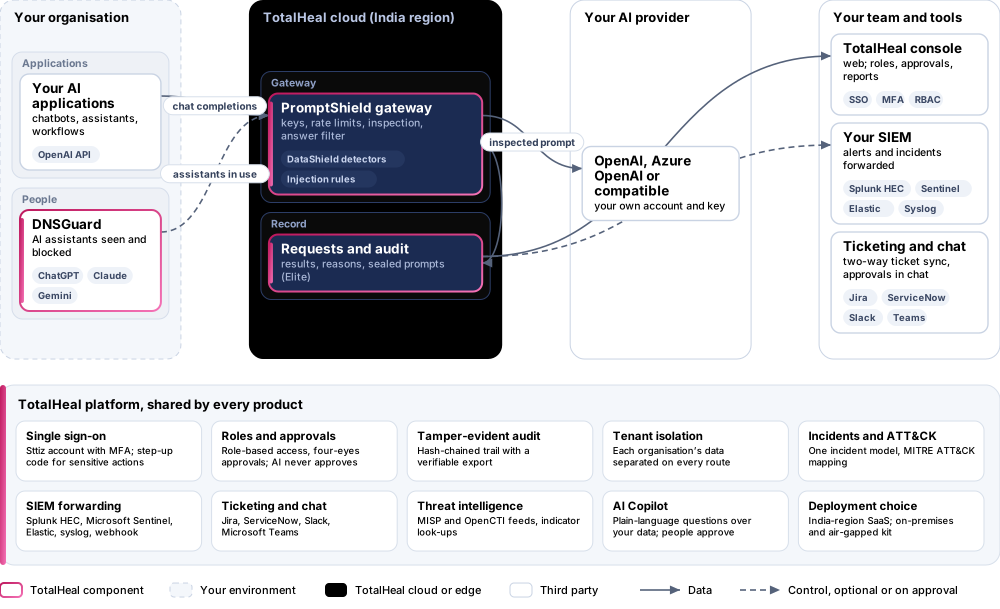
PromptShield shows which AI assistants are used on your networks and lets you sanction or block each one. For your own applications it is a gateway: they call PromptShield exactly as they would call the OpenAI API, and every prompt is inspected before it reaches your provider — sensitive data redacted or blocked, injection attempts stopped — and every answer is checked on the way back.

PromptShield AI Security, feature by feature.
AI assistants in use
ChatGPT, Claude, Gemini, Microsoft Copilot, DeepSeek, Perplexity and other assistants found from DNSGuard’s hourly counts and network-sensor events: how many people, how often, since when. Sanction the one the company pays for; block the rest through DNSGuard on every network.
A gateway that speaks the OpenAI API
Applications change only the base URL and the key. Chat completions and the model list are supported; streaming requests are answered as server-sent events after the answer is inspected.
Your provider, your account
OpenAI, Azure OpenAI or any OpenAI-compatible endpoint — Anthropic’s compatibility endpoint, Mistral, Groq, a self-hosted vLLM or Ollama. The provider API key is kept encrypted and never shown again; requests leave through TotalHeal’s egress guard.
Sensitive data never reaches the model
Every prompt is inspected with the DataShield detectors — Aadhaar, PAN, GSTIN, card numbers, bank accounts and IFSC, passports, cloud keys, tokens and passwords — and allowed, redacted or blocked by severity. The application receives a coaching message to show the person.
Answers checked too
High and critical sensitive data in a model’s answer is replaced before the application sees it.
Prompt injection and jailbreaks
A curated rule set of published attack patterns — instructions to ignore earlier instructions, requests for the system prompt, “developer mode” and DAN-style role play, forged chat-template markers, hidden characters, encoded payloads and data-exfiltration links — scored per prompt; above your threshold the prompt is blocked or flagged.
Per-model policy
Allow only the models you have approved on each gateway, and cap the tokens of the expensive ones.
One key per application
Each application gets its own key with its own rate limit; revoke one without touching the others. Only a fingerprint of each key is kept.
Every request on record
Application, end user, model, result, reasons, sensitive data found (masked), latency and tokens. For regulated teams the full prompt and answer are kept encrypted, and opening one is itself recorded in the audit log.
How PromptShield AI Security works.
PromptShield shows which AI assistants your people use and blocks the ones you have not approved. Your own AI applications call it like the OpenAI API: every prompt is inspected before it reaches your provider, sensitive data is redacted or blocked, injection attempts are stopped, and every answer is checked on the way back.
- SeeAI assistants in use appear from DNSGuard and network sensors within the hour.
- DecideSanction the assistant the company pays for; block the rest on every network.
- ConnectAdd your provider account as a gateway and give each application its own key.
- InspectPrompts are checked for sensitive data and injection attempts before they leave.
- RecordEvery request is recorded; regulated teams keep the full prompt, encrypted.
Platforms and deployment
Platforms
| Platform | How it is covered |
|---|---|
| Discovery and blocking | DNSGuard (cloud or on-premises resolver, desktop agents); NetWatch sensors |
| Gateway | OpenAI Chat Completions API (POST /v1/chat/completions, GET /v1/models), streaming included |
| Providers | OpenAI, Azure OpenAI, any OpenAI-compatible endpoint (Anthropic, Mistral, Groq, vLLM, Ollama) |
| Console | TotalHeal web console |
Deployment
| Profile | Status |
|---|---|
| SaaS (India region) | AvailableThe gateway runs in the TotalHeal cloud and calls your provider from there. |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. |
Essential, Professional or Elite.
Priced per user per year. Counted: people in the organisation covered by discovery and the gateway.
| Feature | EssentialUS$18per user per year | ProfessionalUS$36per user per year | EliteUS$54per user per year |
|---|---|---|---|
| AI assistants in use (ChatGPT, Claude, Gemini, Copilot, DeepSeek and more) from DNSGuard and network sensors; sanction or block each through DNSGuard | |||
| AI gateway for your own applications: OpenAI-compatible endpoint, one key per application with its own rate limit, your provider key kept encrypted | |||
| Prompts inspected with the DataShield detectors: sensitive data allowed, redacted or blocked by severity, with a coaching message | |||
| Sensitive data removed from answers; every request recorded; alerts for blocked requests | |||
| Prompt-injection and jailbreak detection, allowed models and token caps per model, full prompt audit kept encrypted |
List prices per user per year; minimum 25 users. Each tier includes everything in the tier before it. Volume, multi-product and partner pricing on request.
PromptShield is sold on its own, outside the editions; blocking assistants needs DNSGuard.
Government profile. Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks.
What you need
- DNSGuard for discovering and blocking AI assistants
- Your own account with OpenAI, Azure OpenAI or an OpenAI-compatible provider for the gateway
Procurement documents for PromptShield AI Security
The datasheet is public. The full dossier is sent on request, so we can match it to your tender.
- Datasheet. What the product does, platforms, deployment profiles, tiers and honest limits.
- Compliance matrix. Each requirement marked comply, partial or no, with an evidence reference — CERT-In directions, DPDP, ISO 27001 controls touched, accessibility of the console, data residency.
- Bill of materials. SKUs per sizing, the unit and quantity formula, customer-side components and services.
- Architecture and hardening. How the product is deployed and the hardening guidance for each component.
- SLA. Support tiers, response targets the team can meet, update cadence and end-of-life policy.
- OEM authorisation letter. A MAF template for resellers and system integrators, with product names exactly as on the SKU.
Get a quote for PromptShield AI Security.
Tell us how many users you need and how you want to deploy. We reply with a quote and the procurement documents you ask for.
Or email business@totalhealsecurity.com.