TotalHealSaaSGuard
Cloud app discovery and control (CASB)
Shows which cloud apps your people use — generative AI, file transfer, remote access and 100 more — how risky each is, and blocks the ones you decide against through DNSGuard.
- Cloud (SaaS)
- On-premises
- Air-gapped
The challenge
People sign up for whatever gets the job done: a free AI assistant for a contract, a file-transfer site for a large export, a remote-desktop tool for a vendor, a PDF converter for a payslip. None of it is on an approved list, and nobody can say which apps hold company data, who uses them, or whether the one that was banned last quarter is still in use.
The answer
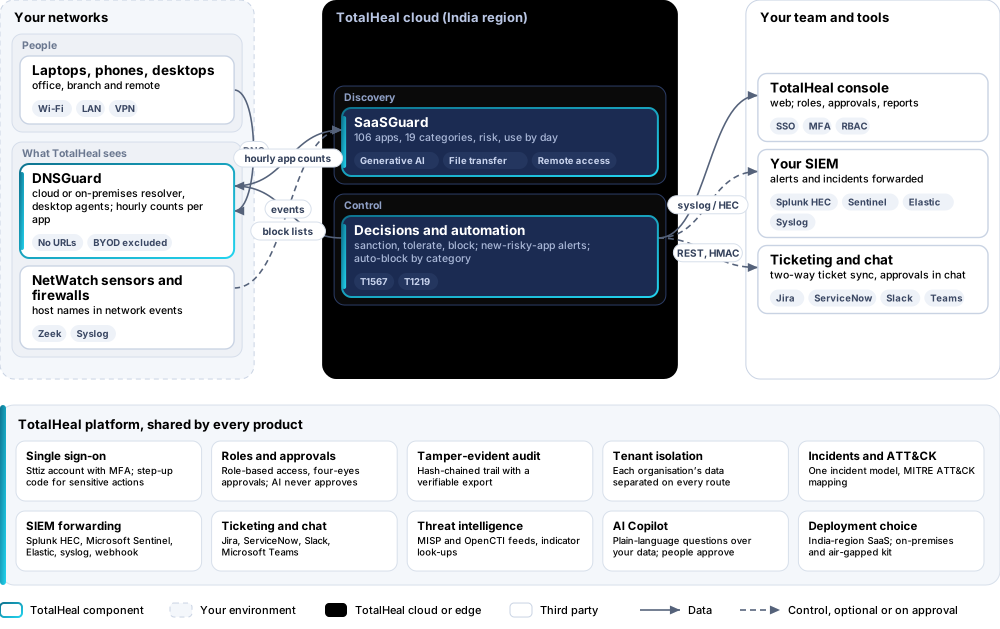
SaaSGuard learns which cloud apps are used from what TotalHeal already sees — DNSGuard’s hourly count per app, DNS logs and the host names in network-sensor and firewall events — and matches it against a catalogue of 106 applications in 19 categories. Each app gets a risk and a decision: sanctioned, tolerated or blocked. Blocking goes through DNSGuard on every network straight away.
- Status
- Available
- Deploys as
- Cloud (SaaS) · On-premises · Air-gapped
- Runs on
- Blocking
- Priced per
- User per year
- Trial
- 30 days, up to 50 users
- Licence
- Sold on its own; one TotalHeal console
Supported platforms
- DNSGuard networks and desktop agents
- NetWatch sensors
- Firewall logs sent to TotalHeal
How it works
- SeeWith DNSGuard on your networks, apps appear within the hour: users, look-ups, networks and use by day.
- ScoreEach app gets a risk from its category and how widely it is used.
- DecideSanction the tools the company pays for, tolerate the harmless ones, block the rest.
- EnforceA blocked app’s domains are refused by DNSGuard on every network and desktop that uses it.
- Stay aheadA new high-risk app raises an alert; categories you choose are blocked the first time a new app appears.
Reference architecture
Key capabilities
- Discovery without an agent or a proxyUsage comes from DNSGuard’s hourly SaaS counts, full DNS logs where a policy keeps them, and the host names in NetWatch sensor and firewall events already in TotalHeal. Nothing new is installed and no traffic is decrypted.
- Privacy by designDNSGuard sends the app and how many clients used it in each hour — never URLs, page content or anyone’s browsing history. Personal (BYOD) networks and policies that log nothing are never counted, and discovery can be turned off per policy.
- A catalogue of 106 cloud appsOffice suites, storage, file transfer, messaging, video meetings, generative AI, collaboration, document tools, translation, e-signature, development, cloud consoles, paste sites and tunnels, remote access, CRM, marketing, web mail, social media and streaming — matched by their domains, the most specific first.
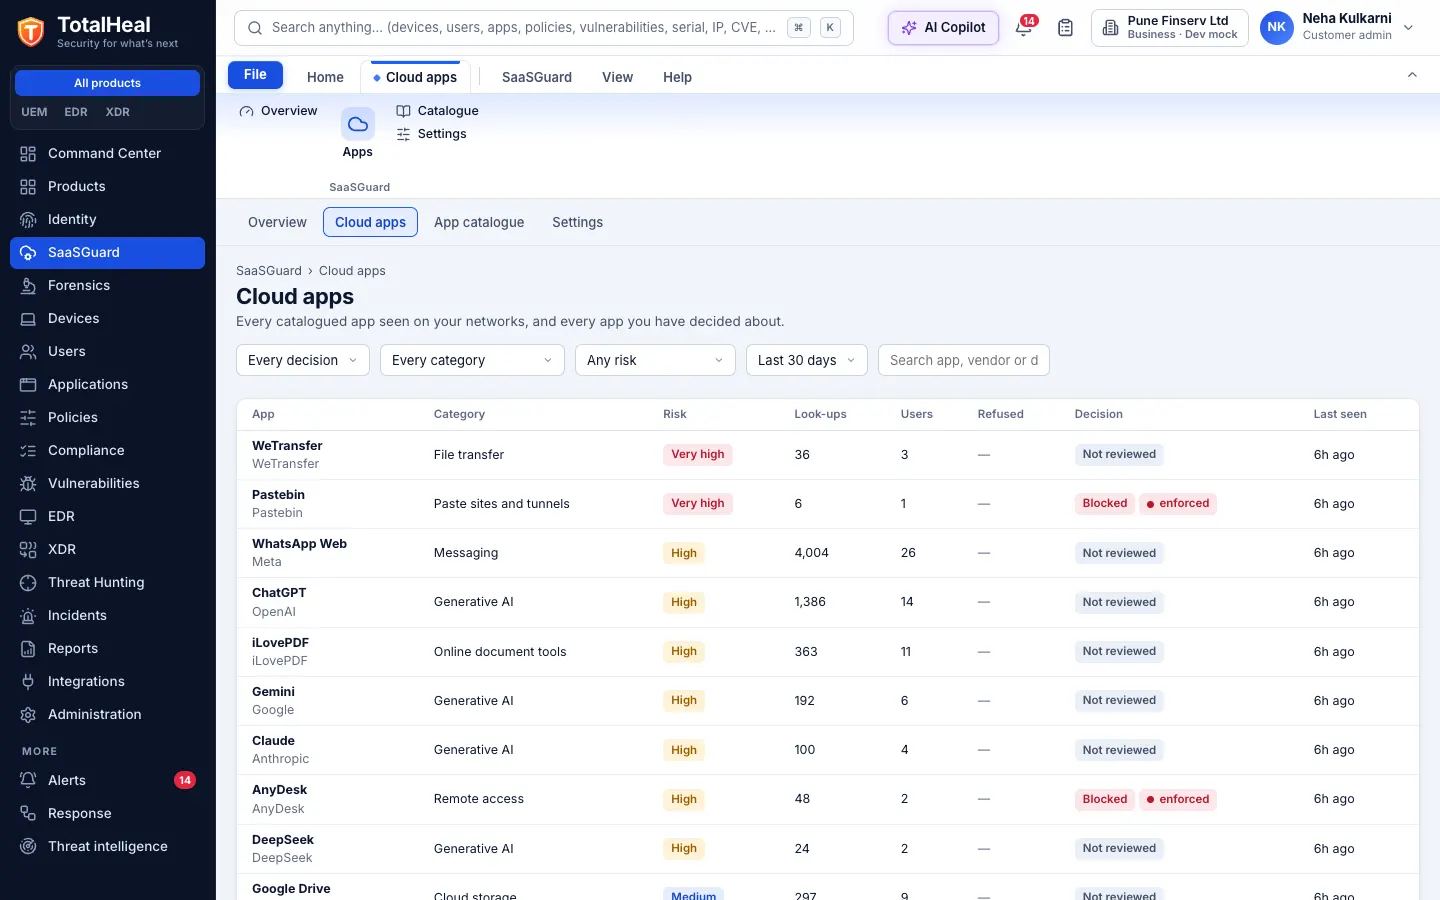
- Risk for every appEach category has a base risk from what it lets data do (file transfer, paste sites and tunnels: very high; generative AI, remote access, document tools: high); wide use raises it, and a sanctioned app is lowest.
- What each app is used forLook-ups, refused look-ups, users, networks, sources, first and last seen, and use by day over up to 90 days, for every app seen or decided.
- Sanction, tolerate or blockEvery decision carries a note and is kept in the audit trail. Blocking puts the app’s domains on the deny list of every DNSGuard policy straight away; unblocking or sanctioning removes exactly the domains SaaSGuard added and nothing an administrator put there.
- New risky apps raise an alertEvery hour SaaSGuard checks for apps used for the first time; a high-risk one nobody has reviewed raises an alert mapped to MITRE ATT&CK (T1567 exfiltration over web services, T1219 remote access software) in the same incident queue as endpoint and identity alerts.
- Block new apps automaticallyChoose categories — paste sites and tunnels, file transfer, remote access — and a new app in them is blocked the first time it is seen. Apps you already decided about are never changed.
- Generative AI in viewChatGPT, Claude, Gemini, Copilot, DeepSeek, Perplexity and other AI assistants are their own category, so you can see who uses them and sanction the one the company pays for.
In the console
Deployment options
System requirements
Protected platforms
- DNSGuard networks and desktop agents
- NetWatch sensors
- Firewall logs sent to TotalHeal
On-premises server
- Operating system
- RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12
- Processor
- 4 vCPU (tested configuration)
- Memory
- 8 GB recommended (6 GB minimum)
- Disk
- 10 GB free for software, releases and backups, plus data
- Sign-in
- Active Directory / LDAP, SAML 2.0 or OpenID Connect
- Software
- Nothing to pre-install: no container runtime, database, web server or Java
Network and access
- DNSGuard on your networks or desktop agents, a NetWatch sensor, or firewall logs sent to TotalHeal
- For blocking: DNSGuard with at least one policy
Alerts and tickets to
- Splunk
- Microsoft Sentinel
- Elastic
- Syslog / CEF
- Jira
- ServiceNow
- Slack
- Microsoft Teams
Technical specifications
| Features | Included | ||
|---|---|---|---|
| Discovery without an agent or a proxy | Included | ||
| Privacy by design | Included | ||
| A catalogue of 106 cloud apps | Included | ||
| Risk for every app | Included | ||
| What each app is used for | Included | ||
| Sanction, tolerate or block | Included | ||
| New risky apps raise an alert | Included | ||
| Block new apps automatically | Included | ||
| Generative AI in view | Included | ||
| Availability by tier | Essential | Professional | Elite |
| Discovery from DNSGuard hourly counts, DNS logs and network-sensor and firewall events: 106 cloud apps in 19 categories, risk, users, look-ups, networks, use by day | Included | Included | Included |
| Decisions per app — sanctioned, tolerated, not reviewed — with a note and an audit trail; app catalogue | Included | Included | Included |
| Alert in the incident queue when a new high-risk app is used for the first time | Included | Included | Included |
| Block an app: its domains go on every DNSGuard policy, and unblocking removes exactly what SaaSGuard added | — | Included | Included |
| Block new apps automatically in the categories you choose | — | — | Included |
| List price per user per year | US$12 · ₹1,140 | US$24 · ₹2,280 | US$36 · ₹3,430 |
| Platforms and coverage | |||
| Sources | DNSGuard (cloud resolver, on-premises resolver or desktop agents); NetWatch sensors; firewall and proxy logs sent to TotalHeal | ||
| Blocking | Through DNSGuard policies, on every network and desktop that uses them | ||
| Console | TotalHeal web console | ||
| Deployment options | |||
| SaaS (India region) | AvailableDiscovery and decisions in the cloud; blocking in DNSGuard wherever it resolves. | ||
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. | ||
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. | ||
| Licensing | |||
| Priced per | User per year | ||
| Counted | People in the organisation whose traffic SaaSGuard covers | ||
| Trial | 30 days, up to 50 users | ||
| Editions | SaaSGuard is sold on its own, outside the editions; blocking needs DNSGuard. | ||
| Government profile | Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks. | ||
| Procurement dossier | Compliance matrix, bill of materials, architecture and hardening, SLA and OEM authorisation letter, on request | ||
| On-premises server | |||
| Operating system | RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12 | ||
| Processor | 4 vCPU (tested configuration) | ||
| Memory | 8 GB recommended (6 GB minimum) | ||
| Disk | 10 GB free for software, releases and backups, plus data | ||
| Sign-in | Active Directory / LDAP, SAML 2.0 or OpenID Connect | ||
| Software | Nothing to pre-install: no container runtime, database, web server or Java | ||
| Requirements | |||
| Requirement 1 | DNSGuard on your networks or desktop agents, a NetWatch sensor, or firewall logs sent to TotalHeal | ||
| Requirement 2 | For blocking: DNSGuard with at least one policy | ||