TotalHealDatasheet · 27 October 2026
TotalHealThreatFusion
Extended Detection & Response (XDR)
One incident across endpoint, network, identity, email and cloud — with or without our EDR.
- Cloud (SaaS)
- On-premises
- Air-gapped
The challenge
An attack touches a firewall, a sign-in and a laptop, but each tool raises its own alert and nobody sees that they are one story.
The answer
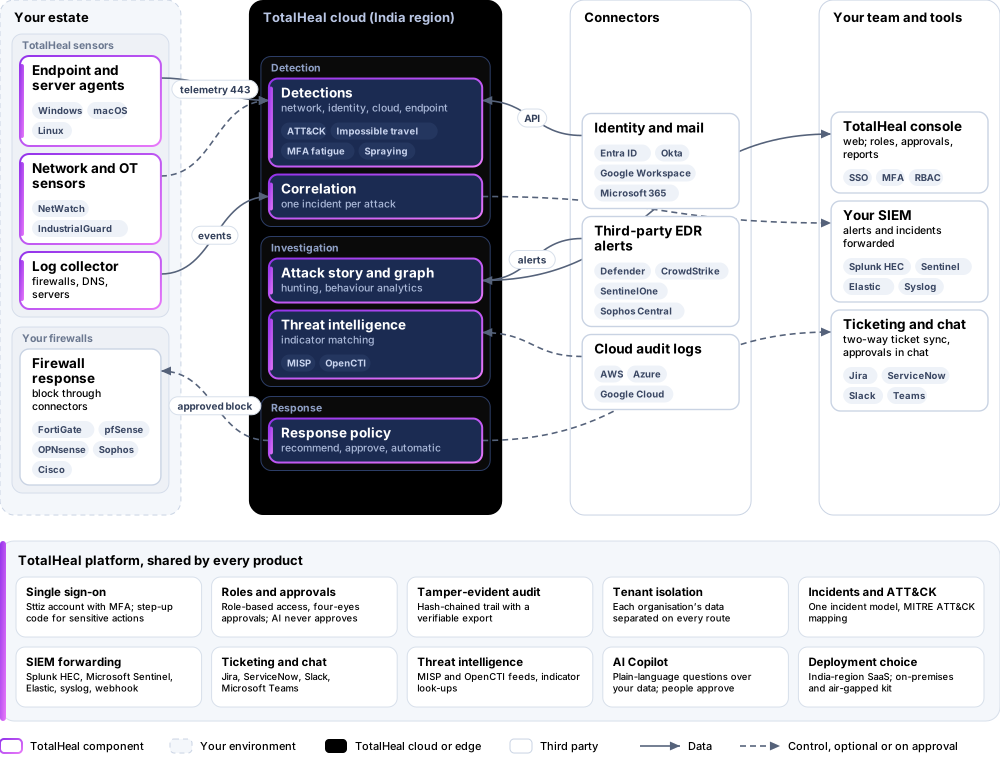
ThreatFusion joins alerts from TotalHeal products, your firewalls and DNS servers (through the collector) and your identity and cloud providers (through connectors) into one incident with an attack story — it does not need TotalHeal EDR.
- Status
- Available
- Deploys as
- Cloud (SaaS) · On-premises · Air-gapped
- Runs on
- Priced per
- Endpoint equivalent per year
- Trial
- 30 days
- Licence
- Sold on its own; one TotalHeal console
Supported platforms
- Windows10 / 11 (x64)
- macOS11 and later
- Linuxx86_64, aarch64, systemd
- FortiGate
- Palo Alto Networks
- Microsoft Entra ID
- Okta
- Google Workspace
- Microsoft 365
- Microsoft Defender
- CrowdStrike
- SentinelOne
How it works
- ConnectAdd any source: TotalHeal agents, the collector or a connector.
- DetectNetwork, identity and cloud rules mapped to MITRE ATT&CK.
- CorrelateAlerts about the same person or host join one incident.
- InvestigateAttack story, security graph and hunting in the console.
- RespondActions run through your response policy and approvals.
Reference architecture
Key capabilities
- Any event sourceTotalHeal endpoints, the log collector, or connectors for Microsoft Entra ID, Okta, Google Workspace, Microsoft 365, the AWS, Azure and Google Cloud audit logs, and alerts from Defender for Endpoint, CrowdStrike, SentinelOne and Sophos Central.
- One incident per attackAlerts about the same person from network logs, sign-ins, mail and endpoints are joined into one incident; tested with a firewall scan and a sign-in brute force against the same user, on an organisation without TotalHeal EDR.
- Network detection rulesThe same firewall and DNS rules as LogIntelligence: scans, denied-connection bursts, threat-intelligence hits, algorithm-like domains and brute force, mapped to MITRE ATT&CK.
- Identity and cloud detectionsImpossible travel, MFA fatigue, password spraying, brute force, privileged role grants, risky OAuth consent and cloud control-plane changes.
- InvestigationAttack story, security graph, threat hunting and behaviour analytics in the console.
Deployment options
Cloud (SaaS)AvailableSingle-region service.
On-premisesAvailableDelivered with our team from the on-premises kit.
Air-gappedAvailableOffline kit, offline licence file and offline update bundles.
System requirements
Protected platforms
- Windows10 / 11 (x64)
- macOS11 and later
- Linuxx86_64, aarch64, systemd
- FortiGate
- Palo Alto Networks
Works with
- Microsoft Entra ID
- Okta
- Google Workspace
- Microsoft 365
- Microsoft Defender
- CrowdStrike
- SentinelOne
- Sophos Central
- AWS
- Microsoft Azure
- Google Cloud
On-premises server
- Operating system
- RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12
- Processor
- 4 vCPU (tested configuration)
- Memory
- 8 GB recommended (6 GB minimum)
- Disk
- 10 GB free for software, releases and backups, plus data
- Sign-in
- Active Directory / LDAP, SAML 2.0 or OpenID Connect
- Software
- Nothing to pre-install: no container runtime, database, web server or Java
Network and access
- At least one event source: TotalHeal endpoints, the collector or a connector
Alerts and tickets to
- Splunk
- Microsoft Sentinel
- Elastic
- Syslog / CEF
- Jira
- ServiceNow
- Slack
- Microsoft Teams
Technical specifications
| Features | Included | |
|---|---|---|
| Any event source | Included | |
| One incident per attack | Included | |
| Network detection rules | Included | |
| Identity and cloud detections | Included | |
| Investigation | Included | |
| Availability by edition | Business | Enterprise |
| Correlated incidents, attack story, network / identity / cloud detections | Included | Included |
| Saved searches and scheduled rules | Up to 10 scheduled | Included |
| Full security graph, correlation studio, detection engineering | — | Included |
| Microsoft 365 and Google Workspace email signals | — | Included |
| Platforms and coverage | ||
| Sources | TotalHeal agents, the TotalHeal collector (Linux), API connectors (identity, cloud, mail and third-party EDR alerts) | |
| Console | TotalHeal web console | |
| Deployment options | ||
| SaaS (India region) | AvailableSingle-region service. | |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. | |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. | |
| Licensing | ||
| Priced per | Endpoint equivalent per year | |
| Counted | Event sources (devices, collectors and connectors) in endpoint equivalents | |
| Trial | 30 days | |
| Government profile | Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks. | |
| Procurement dossier | Compliance matrix, bill of materials, architecture and hardening, SLA and OEM authorisation letter, on request | |
| On-premises server | ||
| Operating system | RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12 | |
| Processor | 4 vCPU (tested configuration) | |
| Memory | 8 GB recommended (6 GB minimum) | |
| Disk | 10 GB free for software, releases and backups, plus data | |
| Sign-in | Active Directory / LDAP, SAML 2.0 or OpenID Connect | |
| Software | Nothing to pre-install: no container runtime, database, web server or Java | |
| Requirements | ||
| Requirement 1 | At least one event source: TotalHeal endpoints, the collector or a connector | |