Network Detection & Response (NDR)
Detecting what agents cannot see, from the network itself
Network detection and response from a passive sensor: beaconing, DNS tunnelling, data leaving, lateral movement and exposed services — no agent on the hosts.
Contents
- 1Executive summary
- 2The challenge
- 3Architecture
- 4How it works
- 5Capabilities in detail
- 6Security and data handling
- 7Where it fits
- 8Deployment and system requirements
- 9Technical specifications
- 10Getting started
1Executive summary
NetWatch reads connection metadata from a passive sensor and detects beaconing, DNS tunnelling, large uploads, lateral movement and exposed services — for every device on the wire, including the ones that can never run an agent.
2The challenge
Printers, cameras, appliances and unmanaged laptops cannot run an agent, and attackers know it. What they do still crosses the network: implants call home on a timer, data leaves in large uploads, and admin protocols move from host to host.
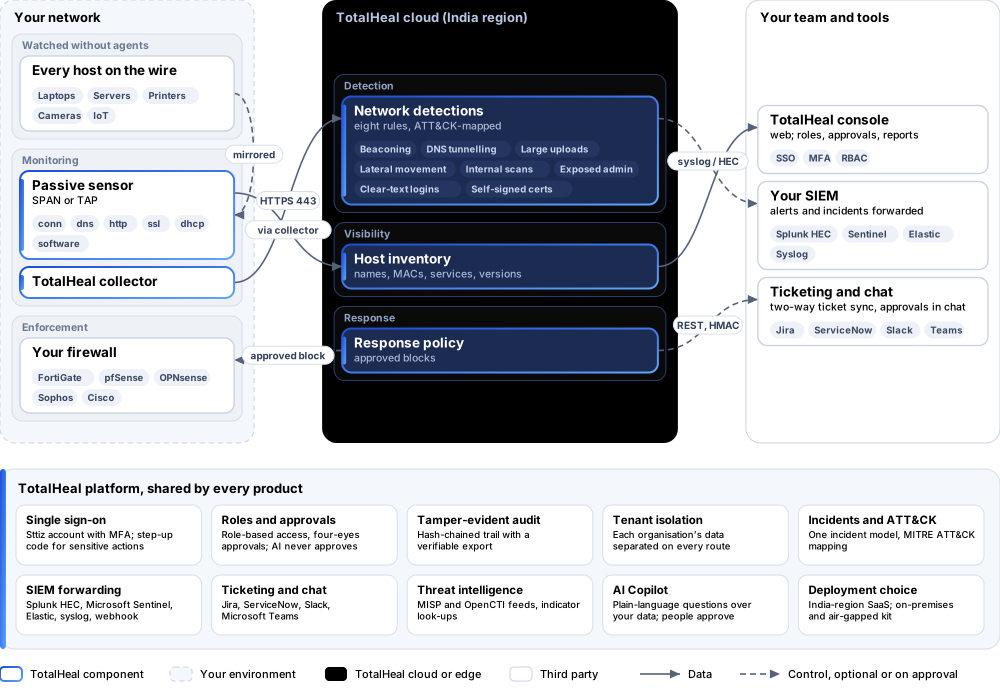
The TotalHeal approach. NetWatch runs on the same passive sensor as IndustrialGuard. It reads connection metadata from a SPAN or TAP port, detects command-and-control, exfiltration and lateral movement, learns a host inventory from the traffic and raises alerts in the same incidents as your endpoint, identity and cloud alerts.
3Architecture
4How it works
- MirrorConnect the sensor to a SPAN or TAP port.
- LearnHosts, services and software versions from the traffic.
- DetectEight detections for C2, exfiltration, movement and exposure.
- RespondBlock through your firewall, behind approval.
5Capabilities in detail
- Passive sensorA Linux host on a SPAN or TAP port; nothing is installed on the hosts it watches.
- Command and controlBeaconing (regular call-backs) and DNS tunnelling.
- Data leavingLarge uploads to outside addresses.
- Lateral movement and scansAdmin services (SMB, RDP, SSH, WinRM) used host to host, and internal scans.
- Exposure and weak protocolsRemote administration reached from the internet, clear-text logins and self-signed certificates.
- Host inventory from trafficNames and MAC addresses (DHCP), services and software versions seen on the wire.
- Response through your firewallBlocking goes through the TotalHeal firewall connectors, behind your response policy.
6Security and data handling
- PassiveNothing is installed on watched hosts.
- Metadata, not contentEncrypted content is not inspected or stored.
- People approve blocksBlocking follows your response policy.
7Where it fits
8Deployment and system requirements
Protected platforms
- Ubuntu20.04, 22.04, 24.04
- Debian11, 12
- Red Hat Enterprise Linux8, 9
On-premises server
- Operating system
- RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12
- Processor
- 4 vCPU (tested configuration)
- Memory
- 8 GB recommended (6 GB minimum)
- Disk
- 10 GB free for software, releases and backups, plus data
- Sign-in
- Active Directory / LDAP, SAML 2.0 or OpenID Connect
- Software
- Nothing to pre-install: no container runtime, database, web server or Java
Network and access
- A Linux host with a SPAN or TAP port
- The TotalHeal collector
Alerts and tickets to
- Splunk
- Microsoft Sentinel
- Elastic
- Syslog / CEF
- Jira
- ServiceNow
- Slack
- Microsoft Teams
9Technical specifications
| Features | Included | |
|---|---|---|
| Passive sensor | Included | |
| Command and control | Included | |
| Data leaving | Included | |
| Lateral movement and scans | Included | |
| Exposure and weak protocols | Included | |
| Host inventory from traffic | Included | |
| Response through your firewall | Included | |
| Availability by edition | Business | Enterprise |
| Passive sensor, eight network detections, host inventory, alerts in incidents | Included | Included |
| Platforms and coverage | ||
| Sensor | Ubuntu, Debian, RHEL-family Linux with a SPAN or TAP port | |
| Console | TotalHeal web console | |
| Deployment options | ||
| Sensor at your site, SaaS console (India region) | AvailableEvents go through the TotalHeal collector. | |
| On-premises control plane | AvailableDelivered with our team from the on-premises kit. | |
| Air-gapped | AvailableOffline kit, offline licence file and offline update bundles. | |
| Licensing | ||
| Priced per | Sensor per year | |
| Counted | Sensors sending to the organisation | |
| Trial | 30 days | |
| Editions | NetWatch is sold on its own, outside the editions. | |
| Government profile | Government is a profile, not a separate tier or price list: the Elite tier with Government defaults switched on — data residency in India, four-eyes approval of policy changes, a distinct approver for every approval-level action, retention of at least 180 days, and the CERT-In and DPDP reporting clocks. | |
| Procurement dossier | Compliance matrix, bill of materials, architecture and hardening, SLA and OEM authorisation letter, on request | |
| On-premises server | ||
| Operating system | RHEL, Rocky Linux or AlmaLinux 8 / 9; Ubuntu 20.04, 22.04 or 24.04; Debian 11 / 12 | |
| Processor | 4 vCPU (tested configuration) | |
| Memory | 8 GB recommended (6 GB minimum) | |
| Disk | 10 GB free for software, releases and backups, plus data | |
| Sign-in | Active Directory / LDAP, SAML 2.0 or OpenID Connect | |
| Software | Nothing to pre-install: no container runtime, database, web server or Java | |
| Requirements | ||
| Requirement 1 | A Linux host with a SPAN or TAP port | |
| Requirement 2 | The TotalHeal collector | |
10Getting started
- A Linux host with a SPAN or TAP port
- The TotalHeal collector
Start a 30 days trial in the TotalHeal console with a Sttiz account. For a quote, an on-premises installation or the procurement dossier (compliance matrix, bill of materials, architecture and hardening, SLA, OEM authorisation letter), write to business@totalhealsecurity.com.